If you’re not using XML-RPC, you should disable it from your site to prevent bots/hackers from hacking your site or slowing down your site with repeat XML-RPC attacks. Usually, the biggest problem with XML-RPC attacks is not that they get in but that they bog down your server with so many blocked requests.
XML-RPC is used to commonly used to connect to your site and blog from an a mobile app or remote publishing service. If you never publish to your site from anywhere but directly in WordPress admin itself, you are fine to disable it!
You can easily block all xmlrpc.php requests using .htaccess to prevent them from even getting passed into WordPress. Don’t bother using a security plugin for this, they’re either slower to process the block or they essentially do the same by adding this same bit of code to your htaccess.
Apache/LiteSpeed servers can paste the following code in your .htaccess file (preferably at the very top):
# Block WordPress xmlrpc.php requests
<Files xmlrpc.php>
order deny,allow
deny from all
allow from 123.123.123.123
</Files>
Quick note…if you need to leave it on for certain IP, you can whitelist your IP and also Jetpack IP’s (if you use it).
Nginx servers can paste the following code into the functions.php (submitted by Regev):
Configure your Cloudflare account for the best website performance (full explanations provided).
If you’ve ever wondered what settings to choose or why someone would chance from the default options, this guide will explain it all for you. (QUICK NOTE: all you need is the FREE plan.)
UICK Cloudflare settings guide
Leave everything on default and check/change the following settings:
DNS – if enabling proxy, do it only for your domain name and WWW record. Can also be for subdomain as well if it leads to a website. Don’t enable proxy for your control panel or anything that points to an external server.
SSL/TLS > SSL – set to “Full”.
SSL/TLS > Always Use HTTPS – ON.
Automatic HTTPS Rewrites – ON, unless you have some things that still need HTTP.
Speed > Auto Minify – check all 3 (JS, CSS, HTML).
Speed > Brotli – ON.
Speed > Rocket Loader – leave it OFF.
DETAILED Cloudflare settings guide
Overview:
Under Attack Mode – usually off. Only enable if you’re getting hacked with tons of fake/bad traffic.
Development Mode – enable if you’re constantly making design/styling changes to your site. It allows you to see the most recent version, otherwise you might see a cached (outdated) version of your site.
Domain Registration – use if you registered domains with them.
Active Subscriptions – choose which plan you want. The FREE is all I ever use.
API (Zone ID & Account ID) – copy this somewhere as you may have to paste it into your plugins later.
Pause Cloudflare on Site – I typically don’t use this. If I want to disable Cloudflare, I check off the proxy (to grey cloud) from the DNS page.
Remove Site from Cloudflare – self explanatory.
Analytics:
How to read this and deciding whether it’s better to have it on vs off.
Traffic – see your traffic, bandwidth usage, how many users and their location.
Security – see how many times you’ve been hacked, where they come from, which crawlers/bots.
Performance – it only shows if you have Argo service enabled.
DNS – shows how many DNS queries get made.
Workers – shows if you’re using any workers.
DNS:
Shows DNS records – up to you to know what you should have and not have.
Enable/disable proxy – click the cloud icon to enable proxy (ORANGE) or disable proxy (GREY). The proxy features are the security and performance features. Basically decides whether all the settings you put on the different pages will take effect or not. REMINDER: disable proxy when generating SSL from your web server or webhosting control panel, then can turn it back on afterwards.
TTL – when having proxy off, I recommend a higher TTL so that your DNS info is cached. Or lower TTL when migrating so that your DNS record changes take effect sooner. This is helpful to migrate without downtimes.
Custom Nameservers – I never bother with this.
DNSSEC – I never use this.
CNAME flattening – I never mess with it.
SSL/TLS:
SSL – I use “Full” because it uses SSL but isn’t strict about it. I don’t use the “Full (strict)” setting because I hear it increases your SSL handshake times, slowing down every request.
Edge Certificates – you are fine with the free shared options. Totally fine, you get a secure padlock and all that. But if for whatever reason, you don’t want a shared certificate…you can purchase business plan ($20/month) to upload a custom certificate or just pay $5/month and get a dedicated certificate from Cloudflare. If you don’t know what any of this means, you are fine with the free one!
Custom Hostnames – I don’t use.
Origin Certificates – this sounds like such a giant hassle when your web server probably already has free Let’s Encrypt certificates. I don’t waste any time with this.
Always Use HTTPS – put to ON.
HTTP Strict Transport Security (HSTS) – I don’t use this. Yes, it theoretically adds better security and speed by enforcing HTTPS on your site but it’s a giant risk if SSL renewal fails for whatever reason (it won’t allow users to visit your without a proper SSL in place). For that reason, I think it’s much much safer off. The busier and more 3rd-party assets you have on your site, the more this might be a risk to use. Then again, it’s not a risk if you know what you’re doing.
Authenticated Origin Pulls – forces visitors to go through Cloudflare proxy instead of bypassing it. But requires extra configuration at your web server. I don’t use it.
Minimum TLS version – leave this on the lowest setting for maximum compatibility with most browsers. Only raise it if you need your website to be compliant with certain security requirements for specific industries (health, legal, government, etc).
Opportunistic Encryption – leave it ON. (It allows TLS for other protocols like HTTP/2.)
Onion Routing – leave it ON. Protects privacy of Tor network users.
TLS 1.3 – leave it ON for best security/performance.
Automatic HTTPS rewrites – leave it ON, unless you have some items that only work on HTTP.
Disable Universal SSL – only used if you’re planning to have dedicated or custom SSL certificates.
Firewall:
Overview > Firewall Event – look at the visitors that got blocked (or challenged) by Cloudflare’s security proxy. You can also filter the list to look for certain traffic.
Managed Rules – enable web application firewall (requires paid service), see explanations of Cloudflares DOS protection.
Firewall Rules – can create custom rules to block, challenge, or allow specific traffic. I never use much as default Cloudflare rules along with my webserver security has worked just fine.
Tools > IP Access Rules – allow/block/challenge traffic via IP. This is the place to whitelist your IP if you get challenged a lot from your own site for whatever reason.
Tools > Rate Limiting – I don’t use it and I think it costs money. It blocks IP’s based on (defined) usage pattern.
Tools > User Agent Blocking – block certain browsers or applications from accessing your site.
Tools > Zone Lockdown – limits certain URLs on your site to only the IP’s that you allow. Most commonly used for “admin” or other protected areas of your site.
Access:
Manage access to applications – I don’t use this at all.
Speed:
Image Resizing – paid service. Not necessary when you have image plugins already.
Enhanced HTTP/2 Prioritization – enable if you have the paid plan.
TCP Turbo – enable if you have the paid plans.
Auto Minify – check all (JS/CSS/HTML). I love to do this from Cloudflare (using their servers) rather than from my site plugins (which uses resources from my own web server).
Polish – paid service, but I’m not sure if you’ll like their exact image optimization settings.
AMP Real URL – for AMP users only. Uses your URL instead of Googles. I think it makes sense to enable, no?
Railgun – really cool service that really does speed up your site. But it often breaks site style/functionality. Test carefully or if you want to be safe, just don’t use it.
Brotli – leave it ON to benefit from superior Brotli compression.
Mirage (BETA) – I don’t have the paid plan but it’s worth a try if you have the paid plan.
Rocket Loader – I feel this often breaks sites and isn’t worth risking.
Mobile Redirect – use this if you need it. It’s a nice service since these redirects would be faster from a Cloudflare proxy than from a website plugin.
Prefetching URLs From HTTP Headers – you should enable it if you have the paid service.
Caching:
Purge Cache – can purge your Cloudflare cache from here, if you didn’t already do it from the Overview page or even from a website plugin. Useful for when you make changes to your site (or assets) but Cloudflare is still caching the old version.
Caching Level – I recommend standard since it’s the safest one that can cache assets with or without query strings.
Browser Cache Expiration – the default 4-hour setting works fine. But if your site doesn’t change its assets often, picking a longer time (2-8 days) would be better for repeat visitors. I probably wouldn’t go too far above that since any changes might take that much longer to refresh in your user’s browsers.
Always Online – leaving it ON sounds good.
Development Mode – temporarily disables the proxy so you can see changes in real time. Don’t forget to purge cache after you re-enable since this feature doesn’t do it.
Enable Query String Sort – very clever feature that’s extremely beneficial for ecommerce sites caching HTML (via page rule). Allows Cloudflare to cache multiple URLs with same-but-misordered query strings as the same page (since they ARE the same). Great for when you want to cache product-filtering pages so that it doesn’t require exhaustive database lookups on your origin server. Can also be used for other types of pages that alter content depending on the query string.
Workers:
This is so freaken cool but I don’t use this at all right now and it shouldn’t concern you at the moment. It’s pretty much advanced stuff you can toy with later when you got lots and lots of time.
Page Rules:
There are a million guides out there of what (and what not) to put here. If you want to be safe, don’t mess with it. Or play at your own risk.
Network:
HTTP/2 – turn it ON if you have the option to.
HTTP/3 with QUIC (BETA) – I signed up for the waitlist and still waiting. Yes, HTTP/3 is all that and a bag of chips. You should get it as soon as you can.
IPv6 Compatibility – turn it ON if you can.
WebSockets – leave it ON.
Psuedo IPv4 – leave it OFF, unless you need it on.
IP Geolocation – leave it ON. It allows your server to track country location of visitors coming through Cloudflare’s proxy. Can be useful for content-filtering or security-filtering purposes.
Maximum Upload Size – left on 100MB for free plans.
Response Buffering – not available for free plans. Speeds up delivery of many small files.
True-Client-IP Header – not available for free plan. When enabled, Cloudflare includes yet another header (more convenient for servers) containing the original client IP. Helpful for reporting, content-filtering, or security purposes.
Traffic:
Argo – Cloudflare premium routing service. Speeds up your DNS times. Many people don’t feel it’s worth it for the price you pay. Probably makes more sense for really large companies.
Argo Tunnel – used to quickly expose any applications or your network directly to the internet without configuring DNS records or firewall/router.
Load Balancing – can use Cloudflare’s paid load balancing service. It seems pretty cheap to me considering the complexity of their infrastructure, but I never tried it.
Stream:
I don’t know about you but I think their pricing is expensive, although could be more convenient than setting up S3 and Cloudfront and all that. If you’re doing a membership site, just stick to Vimeo PRO.
Custom Pages:
Being able to customize all the error pages that are shown to visitors sounds cool, but I don’t need it.
Apps:
Oh, I pretty much salivated at the idea of playing with this page. It’s so cool to see many widely-used applications that can be now be integrated with your site through Cloudflare rather than through a WordPress plugin. Why is this such a big deal? It means those plugins will be processed and loaded through Cloudflare’s servers rather than yours. More speed and less load on your server…HOORAY!
Scrap Shield:
Email Address Obfuscation – hahaha, man they thought of everything! Yes, leave it ON (so bots don’t collect your email off your website).
Server-side Excludes – one of those ‘good-to-know’ features that I’ll probably never use. Really cool that Cloudflare can exclude desired content from “bad visitors”. I leave it ON but haven’t bothered to exclude anything.
Hotlink Protection – it’s OFF by default and for good reason. Usually, people don’t mind having their web images linked to and shared by other sites. Part of the reason may be because they don’t want their images “stolen” but more likely, they just don’t want their web-server to take extra load. But that really isn’t such a concern when your static assets are now server by Cloudflare’s servers. I know I prefer having my content exposed and freely shared all over!
Comprehensive guide on how to recover from server attacks (whether inbound or outbound). NOTE: this guide is written for WordPress users but can be applied to any CMS.
I wrote this security guide to be as helpful as possible. It should help you detect and repair at least 99% of the hacks out there. I repair around 20 servers every year due to hackers, intrusions, and other interruptions caused by attacks. This cheatsheet was originally compiled for my personal use but has since been re-written to be digestible for even newb server admins. (In the midst of complicated server jargon guides out there, I figured to help the community by writing something more actionable for real-world use.)
The only requirement of this guide is that you know how to get to the command line. Also, I don’t cover all nuances of server security here or list every command for every linux distro. I’m more often using CentOS (RHEL) rather than Ubuntu (Debian). It’s up to you to look up alternative commands if that’s what you need.
First thing to do when your server gets hacked…
OH NO! YOU JUST GOT HACKED!! WHAT DO YOU DO?!! WHAT DO YOU DO?!
Usually, you find out your server got hacked because your datacenter or provider has network-restricted you. Or maybe you find out because of failed services, or defaced websites showing malware. It’s a scary situation as you don’t know what’s wrong and the immediate reaction is to panic. What’s most annoying is that it always seems to happen at the worst time (e.g. big project, vacation, wedding, medical illness).
1. Hire an expert
Seriously, don’t mess around. If you don’t know what you’re doing or have critical sites/client stuff, just hire an expert and be done with it. Now is not the time to play DIY. I advise you not to continue venturing on your own unless you really like being an IT paramedic and being responsible for other people’s lives.
2. Figure out what’s being hacked
Is it an inbound attack?
Or is it an outbound attack?
Is it just malware and defaced website or altered data?
How much access did the hackers get into your server? (Just a backdoor/script running from from user directory? Or is it a root-level intrusion?)
Did your webhost or datacenter limit your network connections?
If the damage is really bad, do you have a plan to temporarily restore critical client sites?
3. Be prepared to build a new server
In many cases, if your server is hacked that badly, it’s faster to rebuild a new server from scratch than to waste time trying to find all the hacks and repair all the damaged services and config files in the server. It’s also not wise as you’re not 100% sure whether it’s still compromised somewhere.
4. Restore from backup or no?
Many people get lazy and try to resolve hacks simply by restoring an older backup. Sure, this can work if the data hasn’t changed much. Just restore the backup and then quickly harden your server/sites to block the impending attack. But it’s not an option if you don’t have backups or the backup data has changed since. Quite often, we don’t notice an attack until much later from when the server was breached. So if you notice it too late, the clean backups may have already been overwritten.
Recovering from INBOUND ATTACKS
This is when outside machines/servers are attacking YOUR server. Some of these attacks actually try to gain entry into your server but others only intend to disrupt services by overwhelming your server. Regardless of their intentions (to get in or not), all of these attacks eat up server resources rendering it unable to load your website for real website visitors.
Different kinds of inbound attacks:
Brute force – multiple attempts in rapid succession at guessing your admin passwords and gaining entry through your login pages or other connection protocols (like XML-RPC for WordPress).
Flood attacks – denial of service (DOS), the even stronger distributed denial of service (DDOS), or SYN FLOOD attacks. These attacks specifically target the server on different ports and protocols, requesting many open connections (beyond the server’s limit). It’s the equivalent of mass-calling someone’s phone-line to make it unavailable for legitimate callers.
These attacks can be randomly targeted or specifically-targeted. The random ones are annoying and erratic. The specifically-targeted are most impactful (they don’t stop until your site goes down). It helps to not have controversial material, exposed IP’s on the internet, or making enemies on the internet. Sometimes, you just can’t help it. It might just be because you have an ecommerce site and those make attractive targets.
Detecting inbound attacks:
Server running slow – this is an obvious sign you might getting hacked. Especially if you haven’t changed anything else on the site and traffic is still the same.
Check for high server (CPU) loadgrep processor /proc/cpuinfo | wc -l. Unnecessary if your webhosting control panel already has a GUI for this. Anything at or above the number of CPU cores you have is considered really high (i.e. load of “5” when you only have 4 cores). High CPU usually means an attack at network level (bombarding services).
Check for high memory usagecat /proc/meminfo or top. High swap messages in your control panel at random intervals are also an obvious indicator. Sometimes the attacks will erratic and you’ll just have to scan logs. High memory usually means an attack at software level (bombarding php scripts).
Check connections per IPnetstat -ntu|awk '{print $5}'|cut -d: -f1 -s|sort|uniq -c|sort -nk1 -r. Up to 50 connections from one IP can be normal, anything over 100 is suspicious. If you see many single connections but coming from the same subnet, check 2nd half of this guide.
Alternate commands to check connections per IPtail -n 10000 yourweblog.log|cut -f 1 -d ' '|sort|uniq -c|sort -nr|more and netstat -n|grep :80|cut -c 45-|cut -f 1 -d ':'|sort|uniq -c|sort -nr|more. Use these if the previous ones didn’t help.
Check for syn connectionsnetstat -n | grep :80 | grep SYN
Check logs for failed login attemptscat /var/log/secure (RHEL, Centos, Fedora) or cat /var/log/auth.log (Ubuntu, Debian).
Then ban the most offending IP’s and/or disable the ports and services that are being attacked.
Stopping inbound attacks:
Ban IP’s – you can block the most offending IP’s through your firewall or security plugin. It might also be helpful to install security software like fail2ban that automatically scans your logs and bans the most obvious IP’s. Sure, there are some debates about its efficacy since it may slow down your server and also unable to detect all kinds of attacks.
Disable ports/services (OPTIONAL) – this is another good tactic to remove attacks by taking away their attack point. Just make sure it isn’t a port or service that you’re actually using.
Enable security (firewall) plugins – the point of using security plugins is to block attacks more efficiently than your current firewall solution. Again, the real risk isn’t that these attacks actually get in but that they use up server resources.
Enable security (firewall) services – another way of blocking attacks is to rely on a security service. Usually they operate at the DNS level, and you send all your traffic through their proxy servers so that they can police incoming requests. This is especially important when you have really complicated attacks that low-level plugins cannot handle. For example, layer 7 DDOS attacks are able to send tons of requests to your computer from many different machines. Because it’s a botnet and not just one computer, you cannot ban a single IP. You’d need a much more sophisticated security service (that probably relies on multiple computers) with the capacity to quickly process these requests and let legitimate traffic through without affecting their page load [too much].
I wish I could be more clear about how to ban IP’s and disable ports/services but it really depends on what firewall you have have. The most common ones I’ve come across are:
iptables (command-line)
ConfigServer
ModSecurity
Firewalld
Lua-Resty-WAF
See which one you have and if you DON’T have one, well it’s time to install one then! Then look up its documentation to see: which ports/services are open, where the block/ban lists are, how to make changes. Don’t forget to restart it after you make changes. (Note to myself to update this distinguish between network vs application firewalls.)
This is when there’s a hack or malware script on your server, using your server to hack other servers. Typically, they take over your server, using it and its resources as part of their botnet to target other servers. Pretty malicious and evil, I know! In doing this, they can clever deploy tons of servers to brute force or DDOS for them instead of having to pay for all those servers themselves. It’s very diabolical! And worst of all, aside from using up your server resources, it gets YOUR SERVER and YOUR IP reputation trouble. It’s the equivalent of a criminal using a stolen car to rob banks.
Unlike other hacks, you cannot fix these on your own time. Quite often, I’ll have clients that have a hacked site but aren’t in a rush to fix it since it’s not as important as the others. Well, guess what? These hacks typically cause other server owners and datacenters to complain to your datacenter that you’re hacking them. At this point, your hardware vendor has no choice but to do the responsible thing by limiting YOUR network connections. That means restricting some of your ports and services to limit the damage, which will affect all sites on the server. So sure…it might not be an important site that was hacked but it will affect all other sites. A definite quandary if you’ve got other client sites on there. So what do you do? Fix the outbound attack ASAP and so your datacenter can lift the network restrictions.
Different kinds of outbound attacks:
Same as the inbound attacks but now it’s your server that’s doing the hacking. Brute force, flood attacks, email spam, etc.
But this time, we don’t diagnose it the same way. We don’t look to see how many connections we have with each IP because the idea isn’t to ban other IP’s. The strategy now is to see which illegal processes are running, find out their location, kill them (from running), and delete them. And then most ideal is to find the hole where they got in and fix or remove that vulnerability as well.
Detecting outbound attacks:
Check outbound connectionsnetstat -nputw and see which ones look suspicious. If you see too many lines, try netstat -nputw | less (PS: you can exit less command with q). If you see any “stealth” processes on the right side, take note of their process ID number (aka “PID”).
Can also check for stealth processes directlyps -ef | grep stealth.
Find location of stealth processlsof -p 12345 | grep cwd and lsof -p 12345 but replace 12345 with actual process ID. Now you know which directory to clean. You should also check /tmp directory as stealth processes often run files from there find /tmp | grep -i stealth.
Stopping outbound attacks:
Clean the directory manually (using your eyes to detect bad files), or plugins (like Wordfence) to scan the site.
Check recently modified files within last 24 hoursfind /directorypath -mtime -1 -ls using path to home directory of hacked user account or wherever the hack was. (Of course, change the path or timeframe as needed). More info on adjusting this command here. Then go in there and delete or fix files! (NOTE: if the list of files is too long, you can use the pipe command to output them to a file.)
Change passwords – if you saw backdoor scripts and Adminer during your cleaning process, it’s probably a good idea to change all control panel, admin, and database passwords. If you also used any of these passwords for your email, PayPal, eBay, Facebook accounts…I recommend changing them as well. (Hackers often cross-check your passwords against other online services.)
Kill the process, using kill if you know the process ID (kill 12345) or pkill if you know the process name (pkill processname). This will kill the PID, as well as anybody running the process under that ID.
Find and close the vulnerability – time to figure out how they got in. Almost always, it’s a vulnerable theme or plugin (probably one that has a form in it). Usually you have to check the modified files. But what if you didn’t detect the hack until many days later? Unfortunately, it’s really hard to know as you probably won’t have the time to read all the logs or maybe the logs showing how they got in have already been deleted. All you can do from here is update all your 3rd-party extensions and keep a close eye on the site. If it gets hacked again, immediately check the recently-modified logs.
Recovering from INJECTION, MALWARE, DEFACEMENT ATTACKS
Malware or defacement attacks are usually the most obvious and most low-level ones. You can see it when your website all of the sudden starts redirecting to another site (probably with ads and questionable material), or maybe your site itself is showing ads, weird pop-ups and triggering security warnings. The worst is when they actually change the data in your database, changing your content and even payment gateway API (re-routing incoming payments to their financial accounts instead of yours!).
Different kinds of malware/defacement attacks:
Website redirects to another one
Website has ads or weird messages/content that you didn’t put
Website content altered and now has links in it that you didn’t put
Website redirects incoming customer payments to the hacker’s financial account instead of yours
Website stops working or is broken
Login page hacked into a “phishing page” and sends info from user login attempts to the hacker
In case you’re wondering of how they got there in the first place…WELL, it usually has to do with some vulnerable plugin or theme that you had running on your site. And to be more specific, it’s almost always some plugin that has a form somewhere or allows users to input information. Quite often, these forms don’t properly “sanitize” the data (sanitization means to disallow illegitimate data)…which then allows the hacker to plug vulnerable code into the database (aka “SQL injection”). These SQL injections are used to run commands that can return information like user names and passwords, payment gateway API’s, or output hack code to a php file (backdoor scripts). And of course, these backdoor scripts are usually placed inpublicly-allowed directories like image and upload directories which allow php execution. Why do plugins sometimes fail to sanitize data? It’s either one or a mix of both lazy and incompetent coding.
The thing that many people don’t understand about security: hackers got in because YOU installed or activated some vulnerable plugin that then let them in. It’s not because your security system failed.
Detecting malware/defacement attacks:
Usually pretty obvious as you can see your website functions have gone awry but now is the time to check the usual places. The first 3 steps must because checked and corrected first.
Check htaccess – open it up and see if there are new lines in there that you didn’t add.
Check wp-config (or other CMS config) – open it up to see if the site URL was changed in there.
Check database – if using WordPress, go to the wp_options table and look at the “site address” and “WordPress address” rows. If it’s got the wrong URL in there, change it back. If they changed all the urls in your database (uncommon), you’ll have to manually change all those strings back.
Check theme files – go into your active theme directory and look around for weird files. Also check the functions.php file to see if any malicious functions were put in there.
Check plugin files – same thing as above but in your plugin directories. This option is often not realistic if you have too many directories to look through.
Check uploads directory (or other public directories) – many hacks and scripts will hide (and execute) from these directories because these are open to the public. Would be smart to block php execution from the uploads directory.
Check plugin settings in WordPress – log into your WordPress admin (or other CMS admin) and check all settings to see if they’ve been changed. What you’re looking for is any place where they might have changed sensitive info, like putting their PayPal email instead of yours, putting their logo or site URL instead of yours, having your backups go to their remote storage instead of yours, etc…the possibilities are endless. Be thorough and check everything over carefully!
Checking for base 64 encrypted code – hackers use this to hide their code. So you can’t read and see the exact strings to search for. No worry at all…we learn how to search base64 code below…
Use find and grep to search for these strings. (But beware that there are legitimate uses for base64.):
base64_decode
gzinflate(base64_decode
eval(gzinflate(base64_decode
eval(base64_decode
Stopping malware/defacement attacks:
Run a malware scanner – run something like WordFence as it has the best malware database and also notifies you of which files are changed and which files don’t belong there. Honestly, this should have been the very first step as soon as you can get into your site admin. But I mention all the other since you have to be at least pass over it with your eyes and know how to do some of this stuff manually.
Check recently modified files – using commands I already shared above.
File comparisons – this is so time-consuming and probably not absolutely necessary unless this is a truly critical site and you need to make sure no other hack or vulnerability is on the server. Simply compare side-by-side between current site backup and one from a date you know is clean. If you’re clever, you’ll know how to do this quicker with code editors.
https://hackforums.net/index.php – resource for hackers (you can see what they scheme up)
Recovering from ACCESS BREACH
This is when hackers have gained access into your websites (or web server) and its content. Even scarier is when they have their own admin accounts or gained access to yours, even worse—have root-level access! Server accounts, FTP, database, email, website admin, and so forth. It’s scary stuff!
Different kinds of access breaches:
Website admin – they have admin rights and can change info as they please.
FTP access – they’re able to upload files and scripts to your server, or also download stuff off of it.
Database access – they’re able to download or change data, even inject code into files.
Email access – able to read, or send emails from your server.
Server access – with access to the server, they can do any or all of the above and even take complete control of your server. Once a hacker has root access and enough time, they could theoretically create so much damage and chaos that it’d be much faster for you to rebuild a new server from scratch than to try repairing their damage. The risk is that even if you found 99.99% of their hacks but still left one backdoor open, they could let themselves back in again.
Detecting access breaches:
Check who is logged in (and where from) w, the hacker might be logged in and working as you speak. Take note of the usernames used and their IP location. Most likely if they’ve gotten this far, they’ve gained root access. Do NOT try to kick them out just yet! You don’t know how much access they have and trying to kick them out now might cause immediate retaliation (further hindering your recovery process).
Check login historylast. Useful to see who has previously logged in. Again, take note of usernames and IP location. You should be very suspicious if the login history is empty (that means somebody is hiding their tracks!)
Check command historyhistory, shows you all the recent commands used (also stored at ~/.bash_history). Look for wget or curl commands used to install malicious software/packages. Again, if you see nothing that means somebody is hiding their tracks.
Check for high use processestop, look at the top cpu-use processes. Hackers with root level access typically use as much server resources as possible to hack other servers, send email spam, or mine for cryptocurrency. If you don’t recognize a process, try lsof -p 12345 or strace -p 12345 (replacing “12345” with the actual process ID number). Lsof will show all the files run by a process (super useful).
Check all processesps, ps aux, ps auxf. Each one shows more info than the last. I personally prefer “ps aux”. Here, you can see all running processes and can take note of any that you don’t recognize. TIP: the more often you run this command the better you’ll get at spotting strange processes.
Check network usageiftop shows processes sending/receiving data, along with their source and destination. Any processes abusing your network with DOS or spam will show at the top.
Check listening connectionslsof -i or netstat -plunt, look for any “LISTEN” or “ESTABLISHED” processes that you don’t recognize. It’s good to check for listening processes as they don’t consume much CPU to get noticed in “top” but are used by hackers to send commands to the server. Again: use the “lsof -p” command to look up processes if you don’t know what they do.
Stopping access breaches:
Shut off server, and hire someone – if this is way above your level. Shut off the server and don’t turn it back on until you have an experienced admin there to quickly remove and reseal so the hacker can’t re-access.
Disable SSH from all IP’s except your own – do this after you turn server back on. Make sure you’re the only one logged in.
Block all ports and services – start limiting your firewall and re-allow things one by one only when you’re sure they’ve been verified.
Kill and remove processes – like you did with previous steps.
Change passwords – to everything.
Search for new admin accounts – hackers often create new admin accounts for themselves once they get in. Or they might do clever things like increasing another user’s rights to full admin, or disguising an admin account as an official “support” account for your webhost/software. Look carefully and remove or adjust all accounts. They often create multiple admin accounts if they go through the trouble at all.
Copy everything to new server – I’m sorry but just about everyone will tell you it’s irresponsible to continue working off a previously compromised server. There’s no telling how much damage was done and not smart to risk it. You’re safer off copying everything to a fresh install. With that said, this option is quite drastic and may not be absolutely necessary if your site was only vulnerable at the user-level and some backdoor scripts. The sentiment is more for when people had their server breached at the root/admin level.
I know most of you will be asking this question here but I really don’t want to write a post-in-a-post, so I’ll leave you with a few quick thoughts.
Firewall is best handled at the server level or even DNS level (by 3rd party security service). Using application-level plugins would be resource heavy, slow down legitimate visitors, and not as comprehensive.
Malware scanning is theoretically best (most resource-efficient) done at the server level BUT…the problem is that applications are so complicated within their own plugins and extensions that they need their own application-specific malware scanners to be thorough enough for zero-day attacks.
The best server-level malware scanner is probably ImunifyAV (free) or Imunify360 (paid). With that said, I don’t use it. So that goes to show how much you really need it. I’m sure it’s great for catching little server oddities and email spam and what not. You can use them if you’d like an easy GUI to do your malware scanning and perhaps auto-scheduling options.
The best application-level malware scanner (for WordPress) is Wordfence. It’s got the best signature database, most thorough and protective. Wordfence catches more hacks, malware, and intrusions than any other WordPress security/malware plugin IMO. It would be so awesome if Wordfence could design a server-level plugin to use on WordPress-oriented servers.
Maldet is a total waste of time. I can’t tell you the number of times this thing has failed to find the exact hack causing all the problems. At best, it finds some old hacks in your email files and that’s it. It’s terrible for zero-day attacks or real-world use IMO.
When it comes to firewall plugins, you need SMART [ADAPTIVE] firewall plugins. With a “dumb” [manual] firewall, it doesn’t adapt to attacks and no settings are applied unless you manually apply them yourself. Smart firewalls can read logs and ban IP’s on the fly based on their behavior.
Most security plugins (both server and application) out there are junk. Just plugins with fancy marketing and logos that barely do even as much as the free ones.
The best way to handle website/server security AND prevent attacks and security mechanisms from slowing down your sites…is to use best practices and other typical checklists security tasks. I’ll do a post on that later. Honestly, you should be learning from real sys-admins showing you their favorite security configs. I don’t even consider myself a senior admin…so if you’re trying to learn from me, you’re already doing it wrong!
Here’s another cool way to deal with security vulnerabilities…by scanning for vulnerabilities during the development process. (Cool service: RIPSTECH) The only issue is that it’s probably very expensive and the only developers who would care to use this are the ones being responsible enough with their coding that they probably won’t need it.
Use a real cron job instead of the default WordPress WP-Cron (for better performance and reliability).
What is WP-Cron, what is it used for, and how to use a Linux server cron job instead.
I promise this is all very easy to do and totally worth your time. It might also fix other random issues you’ve had on your site.
ALWAYS use a real cron job instead of WP-cron.
STEP #1 – disable WP-cron from your wp-config.php file
Open up wp-config.php
Add define( 'DISABLE_WP_CRON', true); anywhere above the line that says, “That’s all, stop editing! Happy blogging.”
STEP #2 – create a cron job from your webhosting control panel
Log into your webhosting control panel (cPanel, etc) and find the Cron Jobs function.
Add this line and set it to 5 min intervals wget -q -O - https://domain.com/wp-cron.php?doing_wp_cron >/dev/null 2>&1 (change the domain to yours)
NOTES:
Some hosts may have limits and force you to use longer intervals (30 mins and up). It’s fine, use the lowest one you can. Even if it’s your own server, I think 5 or 10 mins is frequent enough.
If you really need a higher frequency than what your webhost allows, you can either A) get your own server where you have no limits, or B) get a 3rd-party cron service like EasyCron or even Cloudflare workers.
Some guides out there use the server directory path (/home/user/public_html/wp-cron.php?doing_wp_cron) instead of the URL. I prefer the domain version as it’s easier to understand and safer (since actual server directory might be different). I think only benefit for server path version is it’s slightly less server work not having DNS lookups and SSL handshake but it’s not noticeable at all.
You can use WP Crontrol plugin to manage your cron jobs if you feel they’re backed up or stuck. It’s sometimes an issue for bloated sites. If your cron jobs haven’t run for a while, your site may seem slow or crashed while it catches up. Just wait 5-10 minutes and it should work again.
Multi-sites only have to set the cron job for the main site domain. You don’t have to set for each site in there.
You’re done here. Nothing else to do! If if you want to learn more about how cron jobs work, keep reading…
What is a cron job?
A “cron job” is a service built into all Linux servers that runs processes at a scheduled time. (Sometimes called server cron, linux cron, system cron, cron job, “real cron job”.)
These processes are listed in the crontab file on the server. (Usually located in /var/spool/cron for CentOS/RHEL and /var/spool/cron/crontabs/ for Ubuntu/Debian.)
For those curious, the crontab file usually looks like:
I know all that looks scary right now but don’t worry! They’re just typical server scheduled server commands that tell it to do maintenance checks and tasks. For example:
Running daily backups.
Sending out notifications.
Deleting mailbox trash that’s older than 30 days.
Restarting failed services.
Basically all automated tasks are run by the server cron. It simply checks all the time and runs tasks when they’re scheduled. Most of the tasks you see in there are automatically entered by your server. But you can also add your own (sometimes required for certain plugin functions).
15 */2 * * * is the interval part. I would guess this means 15 mins on the hour of every other hour. (e.g. 2:15, 4:15, 6:15)
/usr/local/cpanel/bin/dbindex is the command. Basically if you had to type this command manually in CLI everyday, you can now simply make it a cron job and you wouldn’t have to do it anymore. It will run exactly as you type.
>/dev/null 2>&1 tells the system to discard any errors or outputs, instead of sending them to an error log or emailing you. Useful since this is only an automated task and nobody is actually at the computer to read it anyway.
And what is WP-Cron?
WP-Cron is PHP function built into WordPress that simulates the server cron service.
It doesn’t actually check the server crontab file every second and run its scheduled tasks. It has its own internal “cron handler” file (not actually a file but stored in database) and only checks it when someone loads up the website. Basically, it’s a fake or pseudo cron service. Or as some developers like to say…”not a real cron job”.
Some scheduled “automated” functions you might find in a typical WordPress site:
Comments automatically emailed to commenters.
Backup plugin running every night.
Scheduled posts publishing live when it’s time.
Widgets updating to show the latest data.
How do you think your site “automatically” handles these functions? It does it using the WP-Cron function (which is built into WordPress and runs from the wp-cron.php file). And is triggered every time the website is requested.
This means…every time someone (or a crawler) visits your website…your site runs the wp-cron.php file.
….this can be bad for 2 main reasons:
If your site has MANY VISITS (over 2K/day):
It slows down the server needlessly checking the WP cron list multiple times every minute.
So a high-traffic site with 500 visitors per second would run 500 WP-cron runs every second, not even including typical bot traffic as well!
If your site has NO VISITS (under 100/day):
Your scheduled tasks might not run for long periods. For example if no one (no person or even a bot) visits your site, and you don’t log into the wp-admin area…your backup might not run, etc.
The scheduled tasks pile up until the moment you visit and then it runs super slow on that visit since it’s busy offloading all the backed up wp-cron tasks.
In real-world practice, the first issue is more common for me. It’s that high-traffic sites are being slowed down by excessive WP-cron runs. The latter issue of low-traffic sites doesn’t matter much because low-traffic usually means low importance anyway. You should absolutely disable it WP-cron and use your Linux server cron jobs instead if you have more than 100k monthly visitors.
My favorite commands for cleaning up autoloaded data from your wp_options table.
Why should you remove autoloaded data? It’s because this type of data is loaded on every page load and often contains data that is no longer used (left behind by already deleted themes/plugins) or left behind because WP-cron wasn’t working and some plugins didn’t clean up after themselves.
Get into your phpmyadmin tool from webhosting control panel (cPanel, Plesk, etc) and follow the commands below!
How much difference can autoloads make?
HUGE! Freaken huge! I’ve seen awful bloated sites with many MB of autoloaded data. Cleared it all and the whole site felt so much lighter, both on frontend and backend. Keep in mind y’all, the backend can’t be cached. Cleaning autoloads definitely has a measureable impact on massively bloated sites and one of the advanced tasks that separates pros from non-pros.
NOTES:
Backup your database before trying any of these optimizations.
If your database has a prefix (e.g. “wp_123abc_” instead of only “wp_”), then retype SQL commands below using the prefix “wp_123abc_options” instead of “wp_option”.
1. Check autoloaded data size
SELECT SUM(LENGTH(option_value)) as autoload_size FROM wp_options WHERE autoload='yes';
This one shows you how big the autoloaded table is. Anything above 1MB really badly needs to be cleaned up; I’ve seen sites with even 40MB (no wonder they crashed!). I try to stay below 500kb if possible (although even 1MB is considered OK). If you have 500kb or less, you can stop here!
2. List top autoloaded data entries
SELECT option_name, length(option_value) AS option_value_length FROM wp_options WHERE autoload='yes' ORDER BY option_value_length DESC LIMIT 200;
This will list the top 30 autoloaded data entries in the table. Delete the ones you know aren’t being used anymore. You can also increase the DESC LIMIT 200 to a higher number like 300 or 500 if you want to see more items. Usually the first 10-50 items make up the bulk of your autoloaded data anyway. And it’s usually only a few plugins that are creating most of the bloat. (Although some really old sites may have tons of stuff left over from deleted themes and plugins.)
3. Find specific autoloaded data
SELECT *
FROM `wp_options`
WHERE `autoload` = 'yes'
AND `option_name` LIKE '%jetpack%'
This command is useful for targeting specific plugins that you KNOW for certain you aren’t using any longer. This is great for cleaning up remnants left from old themes and plugins. Simply replace the string “jetpack” with anything else you like. You’ll also notice that many plugins don’t use their full name. For example, items related to “Full Velocity Minify” plugin might be listed with the string “fvm” in the database.
4. Tracking down mystery autoloads
Did you see some giant autoloads but you’re not sure whether or not you can delete it? Don’t you worry, I have a few handy tricks up my sleeve:
Click on edit and look at the data inside. Sometimes they give you a clue what it’s used for.
Search the option name in Google in quotations. It might also help if you type the word “WordPress” or “plugin” or “theme” before it.
You can also try using step #3 above, but search only the first prefix of the option name. For example, if the full name is “wds_service_results” then you can do step #3 but replace “jetpack” with “wds_”. Sometimes, you’ll find the other option names with more helpful data to track down which plugin it is.
Last but not least, you can simply change the autoload value to “no”. (Then change it back if anything breaks, or delete after a month if all is well.)
Johnny’s personal autoload removal list
A list of the biggest autoload offenders that I often run into. If you see any autoloads you aren’t familiar with. Google around to see what they might be related to. Perhaps an old theme or plugin you haven’t used in a while. (Obviously, you should not delete any autoloads for active plugins!)
Plugins with high autoloads
BackupBuddy
Mobi by Phpbits
Revolution Slider (of course!)
Thrive Architect/Leads
cherry_customiser_fonts_google – probably came from some Google fonts plugin
transients – some people don’t realize they have 40mb of transients sitting there! (YIKES!)
SchemaPro
BeRocket
Jetpack
WPMU DEV (and their many plugins)
Pegasus Accelerator WP
Redirect plugins
Redux framework (any theme using this)
Security Ninja
There’s hundreds more plugins with awful autoload…find them all! (Feel free to report in the comments and I’ll add them here.)
I’ve given examples for both “www” and also “without www”. I gave neutral code that works with any site. If you want, you could also replace “%{HTTP_HOST}%” with your domain name. I only have rewrites for Apache htaccess right now. (NGINX servers can try this.)
Add this code above the #BEGIN WordPress line in your htaccess.
Method #1
This one uses less code but has more redirects when you use page tools. It works well but is perhaps slightly less efficient than the second. (I recommend this method for everyone using Swift Performance plugin.)
WITHOUT www (all visits go to “https://domain.com”):
#301 https redirects to without WWW
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^(.*)$ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
WITH www (all visits go to “https://www.domain.com”):
#301 https redirects to with WWW
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^ https://%{HTTP_HOST}%{REQUEST_URI} [R=301,L]
Method #2
My new favorite method, thanks to Nazar Hotsa who’s researched every method and shared this with me. Awesome community guy with tons of enterprise webhosting experience.
WITHOUT www (all visits go to “https://domain.com”):
# BEGIN Redirects
RewriteEngine On
# 301 redirect www to non-www
RewriteCond %{HTTP_HOST} ^www\.(.*)$ [NC]
RewriteRule ^(.*)$ https://%1/$1 [R=301,L]
# 301 redirect to https
RewriteCond %{HTTPS} off
RewriteRule ^(.*)$ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
# END Redirects
WITH www (all visits go to “https://www.domain.com”):
# BEGIN Redirects
RewriteEngine On
# 301 redirect to www
RewriteCond %{HTTP_HOST} !^www\.
RewriteRule ^(.*)$ https://www.%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
# 301 redirect to https
RewriteCond %{HTTPS} off
RewriteRule ^(.*)$ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
# END Redirects
Other ways to redirect?
Some people complained my examples used too many redirects. In that case, you’re welcome to research on your own and try other methods of redirection.
Read below and see which one you like best (beware, they all have their implications):
CDN’s are becoming all the rage nowadays ever since CloudFlare offered their free plan. But now, there are all kinds of micro-CDN’s popping up everywhere. Each with a different set of pricing and services. I won’t go over the differences…all I care about is speed, reliability (HIT frequency), coverage, and ease-of-use.
Here’s a list of CDN’s I’ve experienced and my thoughts on each:
Akamai – fast, but expensive.
Amazon (CloudFront) – annoying name with same initials as CloudFlare. Fast and works well! I use it for loading large files (videos) from S3 buckets.
BunnyCDN – cheap, fast and works! DNS is not as fast as CloudFlare, IMO. I have many clients on this. All are very responsive.
Beluga – I haven’t tried yet.
CDN.net – never tried, but heard about awful/shady billing practices.
CloudFlare – many say they aren’t a true CDN but they perform with similar results…also free and super fast, fastest DNS times out there. I’ve heard many complaints from folks I respect but I can’t help but wonder if all their 500 errors might just be their server. (If CloudFlare’s DNS is reliable in your target areas, use them! Some areas of the world are not routed as quickly and it appears they sometimes send your data from faraway proxy.)
CDN77 – slow! Don’t even bother.
Fastly – great when it works.
KeyCDN – heard great reviews so far. I would try them if I was venturing out for a new service.
MaxCDN (StackPath) – largely considered fast, but expensive. I’ve had some instances were I felt it wasn’t particular fast at all.
Thoughts on choosing a CDN provider
Decide what matters to you:
budget (how much bandwidth you need)
what you want to cache (small static assets vs large assets vs dynamic pages)
coverage (POP locations in the world, and proximity to your visitors)
quality of service (speed/reliability)
If all you need is static assets (images/css/etc), CloudFlare free plan should be just fine. If you want to have the fastest page loads (caching pages as well as static assets), it’s best to have a CDN with lots of configurable page rules.
Those caching big items will prefer fast bandwidth. Those caching small items (images, css, js) will prefer fast DNS times.
Converting to HTTPS/SSL is one of the scariest tasks out there.
It feels like SUCH a big project with a billion little details. Feels like you need to hire a programmer or server expert or someone to make all the edits on your website, webserver, and Google accounts.
Here are some simple steps to manually set up HTTPS and HTTPS redirects instead of using plugins (further slowing down your site). This will give you the proper URLs and fast speeds.
STEP 1 – Install SSL certificate
Either you do this on your own from cPanel or your webhosting panel. (It’s also possible to get free shared SSL from CloudFlare. But you should still be doing it the proper way, which is from your webserver/webhost.)
Can’t do it yourself? Ask your webhost, or programmer or server guy to do it.
SSL’s are free now! – thanks to LetsEncrypt. Don’t let anyone fool you into thinking you need to pay for it! (Yes, it’s true that not all SSL certificates are the same and that some big stores may prefer the fancier kind that shows your brand name in the address URL. Most sites don’t need this.)
STEP 2 – Change WordPress URL to HTTPS
Go to your WordPress settings and change the website address and site address to HTTPS. If you can’t get in there for whatever reason, you can edit wp-config.php.
STEP 3 – Update your database URL’s
This is the part where most people either get lazy or don’t know how to do it. They’ll use a plugin like some “Really Simple SSL” that forces HTTPS or enable the feature from their security plugin. I HATE THIS…don’t install another plugin just for this basic function!
The best way is to do it manually from your database so that all your asset URL’s and internal links use native HTTPS instead of wasting server resources to reload the links in HTTPS.
Back up your database if you’ve never done this before.
Enter “http:” in the top field and “https:” in the bottom field. Please write it exactly as I say…otherwise, if you put only “http” and not “https:”, you risk jacking up all the entries that already have “https”.
Select all tables.
Honestly, editing database URL’s manually is very easy to do but also very easy to completely screw up your site if you don’t know what you’re doing. Please be careful and make backups.
STEP 4 – Update Google Search Console
Update your website settings in Google Search Console and also Google Analytics to use your new HTTPS address!
STEP 5 – Apply HTTPS redirect in your htaccess file
This is the last step. Put whichever code fits the address you want your users to redirect to….HTTPS with or without WWW? Then relax and you are done!!! WOOHOO! (Don’t have htaccess or you’re not on Apache/LiteSpeed? You probably don’t have to worry about this, but do ask your webhost.)
WITHOUT www (all visits go to “https://domain.com”):
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^(.*)$ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
WITH www (all visits go to “https://www.domain.com”):
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^ https://%{HTTP_HOST}%{REQUEST_URI} [R=301,L]
STEP 6 – Resolve any problems (if needed)
Everything should be working. But just in case, here are a few diagnostic steps you can do if the HTTPS doesn’t show green of you don’t get that padlock.
www.whynopadlock.com – this should be your first order of business. Check here and it will tell why you’re not getting a full HTTPS status.
Google Chrome > Developer Tools > Security – another way is to right-click anywhere on the page, then click “Inspect”, then “Security” TAB. Then reload the page.
Most likely, you may still have some assets loading from HTTP instead of HTTPS. Use the search-replace tool again or go through all your theme/plugin settings.
After moving nearly a dozen WordPress speed-up clients away from “managed VPS” hosting services this past month, I’ve decided it’s time to state loud and clear:
MANAGED VPS sucks! It’s slow as hell and way over-priced!
And don’t think I’ve haven’t tried them all!
A2 MANAGED VPS sucks. ($80-160/month)
InMotion MANAGED VPS sucks. ($80/month)
LiquidWeb MANAGED VPS sucks. ($80/month)
And a dozen smaller lesser known ones as well.
Let me tell you all the reasons why they “suck”.
Managed VPS Hosting is Usually SLOW!
“But how can this be?!” you ask. Or the ever popular, “But how do you know?!”
Ha! I know it is because I manage a dozen web clients every week and get to see every webhosting service out there. I routinely come across really awful slow websites only to find out they aren’t on shared hosting plans but MANAGED VPS hosting plans! Looking at their panel, I can see outdated versions of PHP, GZIP/Brotli compression not enabled, no object caching (Memcached/Redis) installed…you wonder if there was ever a human tech overlooking the server build. (I move them to a new webhost and sure enough, the problems go away.)
“But my MANAGED VPS server is definitely faster than my previous shared hosting plan!”
And THAT right there is the reason why the greatest scam continues to con people into it. Yes, I’m calling it a scam. Most people upgrade to managed VPS from a slow shared hosting account. They call their host complaining about speed, and their host blames their site instead saying “your website is using too many resources, you have too much traffic”… blah blah blah…
The friendly tech support says “upgrade to our premium VPS and it will be much faster!” and customers upgrade because it makes sense. Sure the new VPS is indeed much faster than their shared hosting plan but they don’t realize their $80/month VPS is still slower than most true $10/month VPS servers out there.
What the hell is a “true” VPS server?
How to Detect “FAKE” VPS Specs
The terms “true VPS” and “fake VPS” are completely made up. I consider true VPS as plans that show their true specs and “fake VPS” plans as ones misrepresenting their specs to look more appealing to unsuspecting customers. Another way to look at it is “hardware providers” vs “customer support providers”—more on this later!
Let’s learn how to detect this “scam”, shall we?
Linode UNMANAGED VPS – here’s a standard UNMANAGED VPS plan table by one of my favorite hardware providers. You can see how many CPUs, RAM, hard drive space, and other specs are available. Our reference plan here will be the middle plan ($20 for 2 CPU Cores, 4 GB RAM, etc).
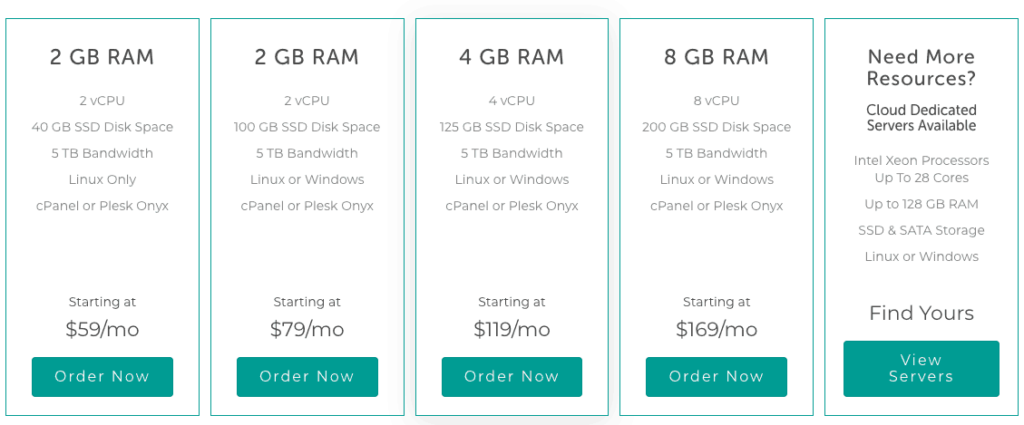
LiquidWeb MANAGED VPS – let the games begin! Here is the respected LiquidWeb, with its managed VPS plans (they promise great hardware AND support). Pay close attention to the middle plan…. 4 vCPU, and 4 GB RAM.
Now ask yourself: what is a vCPU?
Well, I can only assume it stands for VIRTUAL CPU…which means it’s probably not 4 CPU cores at all. Is it even an equivalent of 2 CORES?! From my experience…a $20/month VPS server from Linode or Digital Ocean will easily blow that $119/month LiquidWeb VPS out of the water. Yes, my comparisons are current and yes, I’m 100% dead sure of it.
Whatever hardware they’re using, it’s sub-par compared to true VPS companies. It’s slow as hell and overpriced. Their customer service though is friendly. Whatever you do, don’t be fooled by LiquidWeb’s clever marketing and “technical whitepapers”, no self-respecting systems admin/engineer would use those guys.
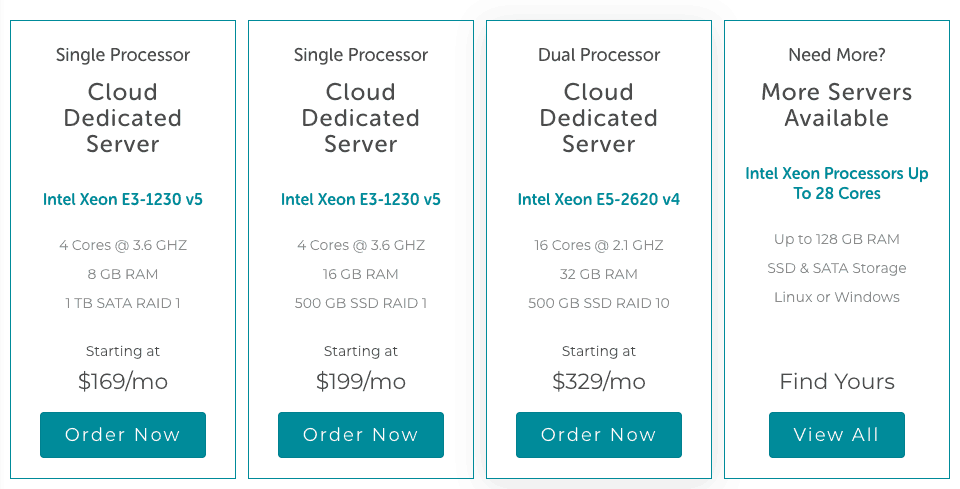
LiquidWeb’s DEDICATED SERVER – oh wait, what’s this? Click on dedicated plans (hardware only, no support) and all of the sudden, they’re giving true hardware specs. No bullcrap vCPU’s labels to be found! They tell you exactly what processor you’re getting and its exact speeds. So what does that tell you?
Not all CPU’s are the same!
A virtual CPU could be equivalent to an actual physical CPU but how would you know?
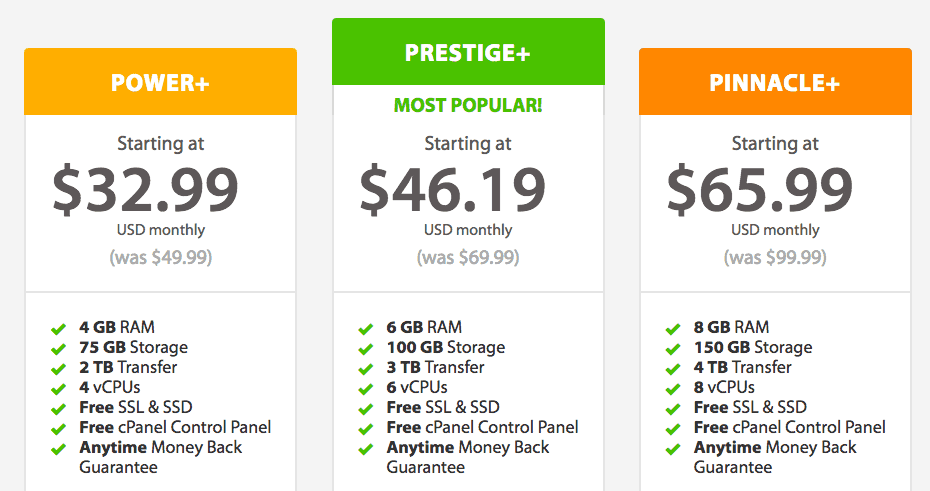
A2 MANAGED VPS – Oh, this one is a classic! Check out the plan on the right side…you get EIGHT (8) vCPU’s for only $65.99/month. I had a client who was so unhappy with it. It wasn’t only a weak server but also terrible support. So much for “managed”. He had a $120/month server with millions of hits every month. The server had frequent downtimes for hours every week and even when it was “up”, it was slow as heck and could barely handle the traffic load. Customer support wouldn’t even acknowledge that it was ever down. He’s since switched to my own private webhosting server and is happy as a clam.
InMotion VPS hosting – ok these guys are a joke! (Just now when I was trying to visit their site, it was DOWN—hahaha!) Anyway, I had a client who was previously on their $80/month plan and so unhappy with it. It was slow as hell and tech support could not fix the problem let alone accept responsibility for it. They SWORE it was his website, and he swore it was their servers.
With my help, he switched to a $20 unmanaged VPS and his website just flew like it never had before. His load time went from 10 seconds to below 1-second! But let’s humor ourselves with the specs for a minute…
Hmmmm…no mention of CPU’s anywhere, which means it’s not a dedicated resource. Their explanation is:
“We allow you to spread your CPU load across all available CPU cores on your server, meaning less time waiting for tasks to be completed on 1 or 2 cores, and more simultaneous processing.”
So this isn’t necessarily a bad thing if they’re being truthful. Will they allow your web traffic to spread across ALL CPU’S on the server? If so, does that mean all other sites have the same benefit and are able to slow down the whole server? Or are they only letting your traffic burst up to a certain amount before hitting the limits? From my experience, whatever they’re offering for $80/month is still much slower than what you get on your own $20/month server.
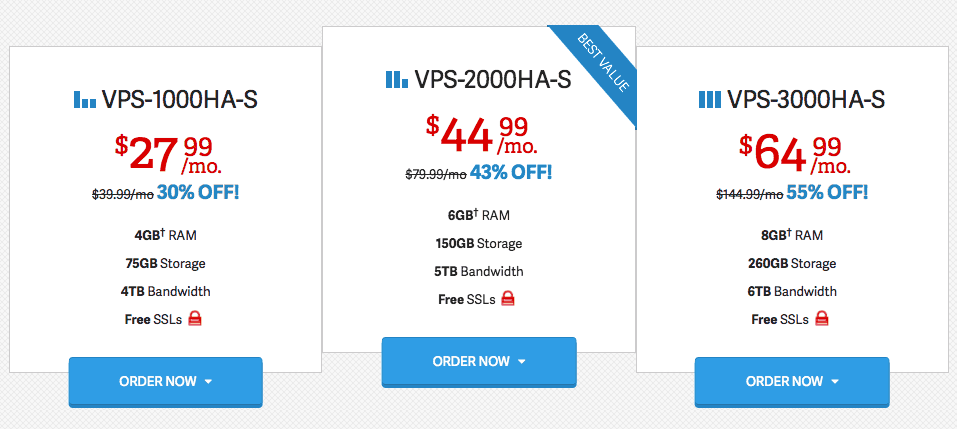
Next up is the storage, 260 GB of storage for only $64.95/month? Guess what, my friend…those gigabytes are sure as heck not on fast SSD drives. Let’s look back at Linode’s UNMANAGED plans…for $80/month, you could have 192GB of SSD storage. And those plans are without any support. So from what I’m seeing here…InMotion is either offering the deal of a lifetime or just not letting you know their hard drives are much slower.
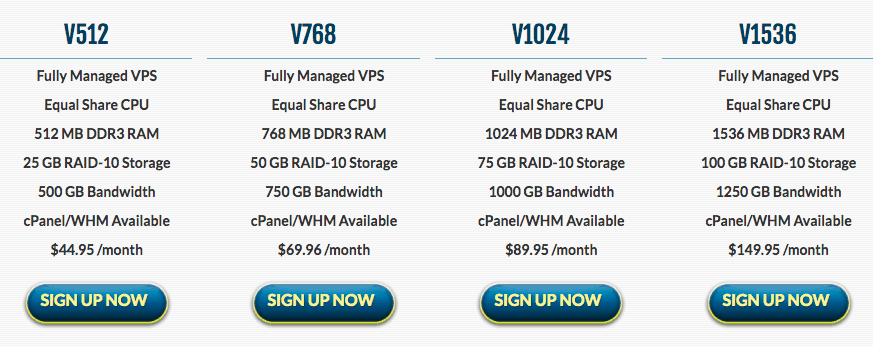
NONAME MANAGED VPS – Ok, this one is REALLY bad. If you could ever get any worse than InMotion, this smaller company has managed it—haha, get it? *I’m silly.*
“Equal Share CPU” means you’re sharing the CPU with all other accounts on the server. Either they’re not giving you dedicated CPU resources, ORRRR, they’re giving you so little that they can’t even put a number to it.
Only 1GB RAM for $89.95?! That’s stingy as hell. How will you ever have enough to cache your website AND power your server applications? This doesn’t even make sense.
75GB RAID-10 Storage – this basically means it’s NOT SSD hard drives! OH NO, their hard drives are gonna be so much slower than everyone else! By the way, if you’ve ever seen shared hosting plans with unlimited hard drive space…that also means you’re getting SLOW hard-drive space, which definitely affects your website speed!
They obviously haven’t revamped their plans since the 90’s and it probably doesn’t matter since they’ve got tons of clients already.
Why Don’t MANAGED VPS Hosts Provide Faster Servers?
REASON #1 – They want to maximize profits.
You would think it’s a total no-brainer of an answer but I’m guessing it just isn’t in their business model. They want you to hit the limit as soon as possible so they can up-sell you on the next faster server. It’s kind of like air travel. The seats keep getting smaller and more uncomfortable every year so that: 1) they can fit more people in the plane, and 2) make money out of the ones who can’t stand the discomfort.
It’s “engineered discomfort!”
And as long as your next server is faster than the previous one, you might not notice that you’re caught in the managed VPS trap. Just so I can give you a reference of how inefficient managed VPS servers can be:
Average $80/month MANAGED VPS – only nominally faster than shared hosting, and can barely handle 50,000 visitors/month. Sadly, many think this server is faster than unmanaged VPS. After all…it sounds better, doesn’t it?
Average $10/month UNMANAGED VPS – with an optimal configuration, can be super fast and can handle 100,000 hits/month. Some crazily aggressive guys can get it to handle even 1 million hits/month!
Managed VPS servers are always going to be optimized to hold as many accounts as possible to maximize profits. And because their servers are set up that way, you’ll always have fewer resources (CPU/RAM) to make your sites truly fast.
And I haven’t even spoken about the configurations. Large companies deal with the volume. They have tons of servers so they don’t spend the time to do any custom configurations for each one. They just load stock settings and move on, with no performance tweaks or anything!
REASON #2 – MANAGED VPS are “customer support” companies.
Remember? MANAGED VPS is really just selling you support, not hardware. Most of the money you’re paying goes to a guy setting up the server, and another one to answer the phone/email/chat when you have problems. When you buy UNMANAGED VPS, more of the money you pay goes to the hardware…this is why unmanaged VPS services are always faster for the dollar.
MANAGED VPS is for non-techy customers who just go by numbers, the higher the numbers the more they can charge. If your server is slow, the support will tell you to upgrade.
UNMANAGED VPS is for true server/tech guys who know technical specifications and configuration details. If your server is slow, the support will show you a bunch of tests and show benchmark numbers to prove how fast their hardware is.
REASON #3 – Managed VPS plans to market to non-techie customers who don’t know any better.
I’ve had friends tell me, “Company XYZ is great! They guarantee how much resources, CPU/RAM/HD you get!”
You would think with clearly defined numbers like that, it’s impossible to get ripped off. But think again…
CPU speeds – are not equal. Intel 3ghz cpu from 2015 is not the same as the Intel 3ghz CPU from 2018. Split it in half and it can be very different for each tiny part. In fact, some 2.5ghz CPU’s are much better than other 3.0ghz CPUs. Same with ram…not all ram is equal.
Cores – some providers say 4-CORE CPU and they really give you 4-CORES. But others like A2 VPS say things like 8 vCPU, which means they give fewer CPU’s but split them virtually to resemble 8. I don’t have a problem with virtualization except for when it’s used to mask how little resources they’re actually giving you. Sometimes you do get the promised number of CPU’s but they’re shared with other accounts.
Memory – is it truly fast memory, and is it dedicated to only you? Are you even sure it’s ALL memory? Some sneaky hosts will give you half-memory and half-SSD hard drive acting as memory. Yes, it’s really shady and makes it that much harder for honest hosts to measure up against them. Most beginners will pick 8 CORES for $60/month over 2 CORES for $60/month. It’s a no-brainer, numbers matter to them.
Hard drives – are they slow drives or fast SSD drives? (Even SSD ranges a lot in speed…just like cable internet…it varies a lot.)
Bandwidth – they might say unlimited but is it really? There’s always a limit somewhere.
ANALOGY: let’s pretend you were outsourcing overseas, and paying for 10 workers (CPUs) at $10/hr each. How do you know what you’re getting?
Is it 10 skilled workers? Or unskilled/child/indentured workers?
Is it 10 dedicated workers? Or workers multi-tasking with other client projects?
Is it really 10 workers? Or just 5 workers doing (2) separate jobs each?
Does each worker have their own machines? Or do they share the same 2 machines and have to take turns?
Just because the company says “10 SUPER-FAST CPU’S” doesn’t mean it is so. There are a dozen ways to cheat the numbers.
Here are some good TECHNICAL QUESTIONS:
BURST CAPACITY – does the account let you burst? What if for a split second, you use up double or triple your allotted CPU/MEMORY? Will they allow that extra traffic, or do they show traffic errors to the other visitors? (This is horrible if your traffic comes in spikes.)
STACK CONFIGURATION – how precisely is the server tuned? Apache on default settings is easily 3-5 times less efficient than properly-tuned Apache. 2-core CPU/4gb ram with expert configuration will easily beat 4-coreCPU/8gb ram with default configurations. What about more performant servers like LiteSpeed or NGINX? What versions of php or mysql is provided? What about object caching modules such as Memcached or Redis?
TRAFFIC/BANDWIDTH – some providers off “unlimited traffic” or a high amount like 1 million visitors, but do they take your website into account? They might mean 1 million “low impact” visitors.
HOW MUCH MANAGEMENT – I highly doubt for $100/month, that you’ll get even an experienced sys-admin to proactively tune your server. They’re so busy fixing issues, they most definitely aren’t going to look at your server unless there IS an issue.
REASON #4 – Most webhosting customers don’t have a point of reference.
How fast IS fast?
Is it 1 second? or 2 seconds? Most of us have a limited understanding of what fast really means. Many of us never defined it, it’s just a perception we have about websites. “Fast” means it feels fast. And “slow” means it takes a couple of seconds. And for most people, “fast webserver” means faster than their previous one.
See, that’s part of the problem. For server administrators, “fast” means 1-second loads or less. For me, “fast” means instant load. End-of-story. If the site doesn’t come up immediately, I can’t stand it. If anything, I would say all web-servers should be able to load your site within 1 second (if it can’t, it’s grossly underpowered). The only reason why you would need a bigger server is so you can handle more traffic!
So for me, bigger servers are for higher traffic/load capacity and not so much about speed. Even a $20/month VPS server should be ultra-fast for most of us.
How to Buy MANAGED VPS
Ok, not all managed VPS services are overpriced. Just most of them, that’s all. If you can find a reputable host with excellent performance reviews and transparent disclosures about their systems, great!
One of the safest ones I’ve found so far is Runcloud or Gridpane. The only issue is they’re not meant for total newbies. Give them a try, I think you’ll be shocked at how much faster their $20/month servers are compared to $80/month servers from other companies. If you want a truly managed VPS, you can look around at some other companies.
Want to venture into UNMANAGED VPS?
They are not for the faint of heart but I can certainly give some tips in another guide.
What managed VPS does is give you a pre-tuned hosting environment that fits most sites out there (with varying levels of aggressive caching enabled). If you’re coming from shared hosting, any VPS will be a noticeable performance gain to you. But where managed VPS can be a turn-off is the price. You might pay upwards of $30-500/month for a server that you could have leased yourself for a quarter of that.
Think of it this way, $80/managed gets you either:
6-core server unmanaged VPS and you have to set everything up yourself, or…
2-core VPS with everything pre-configured, or…
shared hosting account on premium managed VPS (like WPengine).
Most techies will choose the 1st option and set-up the server themselves or hire a cheap sys admin somewhere around the world to provision it for them. (“Provision” is the sys-admin word for ‘setting up a server or network component and providing access’.)
The route of going unmanaged is indeed much cheaper and potentially offers superior service/functionality in the long run since you have full control (but also full responsibility) of everything. Being that you don’t plan to learn any bit of server management, it’s not a bad idea to always have a programmer and sys admin you can hire from time to time to manage this for you. You’ll only need them a couple times a year and you save more money paying them only when needed rather than to pay a managed VPS company a ton of money upfront.
However, some folks really do prefer the convenience. It’s like choosing to build your own PC vs buying a Dell/Apple and it comes with warranty. Given all things equal, it’s always cheaper and better performance to build things yourself.
About 98% of the shared hosting services out there suck!
The bigger and more well-known the company, the more likely it is to suck. It’s slow, it’s insecure, it’s missing features you need, the tech support doesn’t understand your problem (or even your English), or the server keeps going down.
Why is shared webhosting always like this?! (Answers to these galactic mysteries lay inside…)
SHARED HOSTING PROBLEM #1 – Slow Speeds
SHARED hosting = SHARED resources
Imagine being in a crowded apartment building. Noisy neighbors, limited space, lack of privacy, potential security issues, have to share everything. Always having to wait your turn for the laundry machines, someone hogging the hot water, mailboxes sometimes unsecured, can’t park your car however you want. Want to change something in your own apartment? You need permission from the landlord first. Lowest quality carpeting, paint, windows, and other amenities (if it’s even included at all).
That’s exactly how shared hosting is—thousands of low-paying customers crammed into one server. Realistically speaking, what do you expect to get for $5/month? Either a really weak server or a powerful one but shared across many customers. And it’s not just the server, but also the server maintenance and then customer support to be there whenever you need help. So maybe only $2 of your monthly fee actually goes to the server. And then how many sites do you have? Most of these shared hosting servers let you have as many sites as you want, which for many shared hosting accounts can be 10-20 sites. So you might be paying only $0.20 cents per month, per site. Now let’s contrast this to the big corporate companies that pay thousands of dollars to host just their one site. Big difference in quality, as expected.
AWFUL neighbors
This is probably the biggest problem in shared hosting for both the webhosting company as well as webhosting clients. You always have that one awful neighbor ruining it for everyone else. There’s some guy sending spam and getting the server IP blacklisted (causing your emails to hit the spam box as well). Or there’s a guy using his $5/month account to run a huge business…hogging all server resources. Or there’s someone using totally outdated software, making himself and everyone else on the server more vulnerable to hackers. Guess what happens when these neighbors run amuck….the webhosts mitigate this by putting cages on everyone’s account, throttling back their performance.
OUTDATED hardware & software
For the pennies you pay, do you really think that server is gonna have the latest and greatest CPU/memory/hard drive, software, latest PHP, latest Apache modules, and convenient 1-click solutions for all your needs? Of course, not! Most shared hosting servers are like 2 iPhone models behind the top guys.
Sure, if you’re lucky and just found a company starting out, they’ll be more updated than the others. The truth is, they prefer only to update when they absolutely have to. Most of them will run old software for a few reasons: one is to save money on maintenance, and another is to maximize compatibility for different software or different versions. Shared hosting is a high-volume business, remember?
EXTERNAL databases
Quite often the databases are not on the same machine. They’re on another server. Sure, the external database might still be in the same data center or nearby but it’s still an extra proxy and an extra connection time.
“But not all of them are slow!”
This is absolutely true. Not all of them are slow. The same goes for renting an apartment—not all apartment tenants are awful, and not all apartments are crappy. But the saying remains, “You get what you pay for.” and it’s always held true in the long run for me.
Sure, your account might be the first one on a large unfilled server. Or you’re on a server with mostly “quiet tenants”. Or maybe you getting great service from a company just starting out. Sooner or later, the law of economics and sustainability kicks in. Either the performance or maintenance or support suffers somewhere…or the best thing that can happen—is prices go up (quality stays the same).
SHARED HOSTING PROBLEM #2 – Frequent Downtimes
Shared hosting goes down often, unlike VPS/Dedicated servers
It happens ALL the time. It’s something very unique to only shared hosting accounts, and almost never for VPS or dedicated servers. Shared hosting can go down anywhere from a few minutes a month to hours every week. Even the best ones may be fine for a year and then have rampant downtime for 2 or 3 months straight. It’s the industry’s dirty little secret. So why the downtime?
Frequent restarts
Anytime you have tons of different software fighting for CPU, memory, and storage resources, there’s bound to be a crash. Some software might hog all the memory. Some sites might lock up the CPU. A PHP thread might be left open or the database can crash. Maybe a backup function got stuck. Or somebody’s error log ate up all the disk space. It’s not like the software is so primitive and can’t account for all these scenarios, it’s just that you have way too many things going on at once. It’s like asking a parent to watch 30 kids instead of just one kid.
So what happens when something goes wrong and the server locks up? Sure, you can spend some time trying to fix the issue (and risk hundreds of tech support complaints), or you can just restart the server before anyone notices the problem, and act like it never happened. Bandaid solutions are the norm in the shared hosting industry. Just keep the server running and most clients will be ok with that.
Slow maintenance restarts
The other reason for restarts—is maintenance. All servers need to be maintained. At the very minimum, this means security patches to close up known software vulnerabilities. But there’s tons of maintenance that goes beyond that, updating or adding new software models. Tweaking software configurations. Or maybe replacing failing hardware like old disk drives and power supplies. Now here’s a good question…do you think shared webhosting companies update the servers as often as possible? Or do they let the updates stack up until the server is 3 months behind in updates? The longer you wait to fix and update things, the longer it takes to do it. Let’s not forget, these are probably not the newest and fastest servers, right?
Suppose I was a high-end webhosting client, most webhosts would provide a clone server or some kind of backup to prevent any downtimes. But for a $5/month shared hosting account, NOPE! They just shut it down, take their sweet time and it comes up whenever it comes up. And they’re not gonna answer your ticket until it does because they know better than to waste your time. It’s going to be 15 support requests from you saying, “Where’s my server? Where’s my server?!” And then 6 hours later, a small reply of “Server was down for maintenance. Your site is working now. Have we fixed your problem? Please give us 5 stars.”
SHARED HOSTING PROBLEM #3 – Low-Skill Tech Support
Most shared hosting support can’t fix serious problems.
This is a tough dilemma for shared hosting companies and customers. When it comes to most tech support, the REAL TECHIES are the “Level 3 – Tech Support” guys. Level 1 is just a bunch of low-level “customer support” staff. They answer chats, emails, and phone calls. They ask you for your name and account info and then read from a script. Anything they don’t know, they look up on Google first. Some of them probably know even less than you do about web technology but here they are…serving as “friendly fast tech support”.
They’ll go back and forth with you on a few exchanges, writing down your information but the truth is they can’t fix half your problems. They have to ask someone else and then follow up with you a day later. For the money you pay, it’s not possible to have truly skilled systems engineers answer your relatively basic questions right away. They’re probably undermanned and have tons of server issues to tend to.
SHARED HOSTING PROBLEM #4 – Limited Features
This is not actually a problem. You get what you paid for. But it’s important to know what you’re not getting.
Outdated PHP – some hosts offer the latest PHP 7, and some don’t. It should be the standard now but it isn’t.
Uncommon modules – there may be some uncommon Apache modules that are needed by your plugins. If you’re lucky, your webhost has it or is at least willing to install it. If you’re not lucky, they say “NO!” and you’ll have to move to another webhost.
No Memcached/Redis object caching – these PHP extensions can make a huge difference in performance (especially for ecommerce). Unfortunately, they eat up valuable memory and so hosts don’t allow it.
SHARED HOSTING PROBLEM #5 – Security issues
Security issues with data vulnerability
Data vulnerability is perhaps the biggest security issue for most people; imagine someone accessing your server, and seeing all your files and database information. Shared hosting servers aren’t always updated with the latest patches. Old PHP software, old MySQL, older cPanels that haven’t been updated in a year. There’s also the issue of not properly isolating each account. So your account could be hacked into if your neighbor’s account was compromised. How annoying!
Why do some webhosts have this problem? Simply by not backing up the server or lazy setup and maintenance habits that leave holes for hackers to squeeze through. With that said, no server is 100% hack proof. Any hacker given enough time and resources WILL get through. The idea is that you trust your webhost to at least make an effort and slow them down to the point where it isn’t worth it for them to target your server.
Security issues with performance
This is a lesser-known issue with security problems. It isn’t so much about hackers accessing your data but about them affecting your server performance. Quite often, that’s ALL hackers want to do…bring down your server. It’s like that kid pulling the school fire alarm…while he isn’t causing any real problems, he’s still wasting resources. In the server world, hackers can easily bring down your server with DDOS attacks or brute forcing or somehow in some way, overloading it with so many requests that the server gets so backed up, it can’t serve any more webpages.
I think DDOS is best handled with software and manual implementations. It doesn’t that much time, money, and effort but it does take some effort. While some webhosts care about this, others don’t.
SHARED HOSTING PROBLEM #6 – Upsell Business Model
And this here lies the other secret truth about the shared hosting industry. It’s all about the upsell! They’re not gonna give you the best webhosting for your money. They’ll give you great service, but just good enough servers. At some point, you’ll ask them for faster speeds and THAT’S where they make their real money. As with many other businesses, it’s all in the upsell!
The upsell is usually either the $30 “Premium Hosting Plan” (basically still shared hosting but on a less crowded server), or it’s the $50-80 “Managed VPS Plan” where they claim to give you this incredible server that you have all to yourself. And guess what, the same company that sold you those plans is not going to maximize them either. They’ll hope you outgrow it soon and they’ll upsell you again to a bigger plan!
SHARED HOSTING PROBLEM #7 – Fineprint
This is a major issue for many large corporations. They cover their asses, legally, so to speak. Tons of fine print in the contracts where they don’t have to honor any of their marketing promises.
99% UP-TIME GUARANTEE? – there’s probably somewhere in the contract that says they’re not responsible for “unforeseen circumstances”.
FAST WEBHOSTING – but they can just blame your site for the slowness instead of their servers.
SHARED HOSTING PROBLEM #8 – Upfront payments
Webhosting companies are usually high-volume profit-driven machines. Which means a lot of their work goes to driving profit. You would think that means having the best webhosting service and what not but it’s far from that. Their biggest efforts go to marketing and promotions, huge affiliate networks and commissions.
You sign-up for the year and guess what happens after the first month? The server slows down as they pack more customers onto it, and service just gets worse. You’ve already paid the money and locked yourself into a contract so what incentive do they have left to keep you happy? Whatever negative review you might make will be drowned out by the tons of affiliates and corporate partnerships they have out there. Give up all your money too early and the ball is in their court to stretch that dollar as far as they can.
Why Webhosting Sucks
It’s not just shared hosting, VPS can suck too! Any webhosting company can suck! They suck when they care more about profit than quality. They suck when they get acquired by bigger (and less personable) companies. They suck when the industry pivots in a direction they can’t adapt to. All industries, not only webhosting, are prone to shady business practices.
If you want true quality hosting, either:
Pay premium pricing for a proven company.
Be prepared to change webhosts often when their quality drops.
Best WordPress Hosting Reviews in 2026 – Pro Speed Guy
All the WordPress web hosting companies I’ve personally tried or heard about from people I trust!
My comparison criteria are SPEED, reliability (up-time), FEATURES (easy to make changes, add SSL?), and PRICING (not crazy expensive). Customer service is not as important for me since I can do 99% of things myself.
I’ve used nearly all of these web hosts myself (via clients) across a broad range of websites — from small blogs or portfolios to big shopping sites, database-intensive forums, or large portals with many tracking/ad/conversion scripts running.
Good Webhosts
Shared Hosting (cheapest, but functional)
SiteGround – most popular and considered top of the shared hosting tier. Fast, good features and support! The GoGeek plan starts at $11.95 but renews at $35/month making managed hosting or unmanaged cloud far more attractive. (Their built-in SG Optimizer is meh, use SWIFT LITE for best results.) A2 is now becoming the favorite low-tier company due to SiteGround’s recent resource limits.
HostArmada – low cost, good performance, and skilled and friendly 24/7 support. An awesome service and compares favorably (better service yet lower cost) against other shared hosting companies.
ScalaHosting – low cost, reliable service along with helpful 24/7 support. They offer low-cost VPS hosting as well under their proprietary SPanel (which saves on the usual WHM/cPanel costs). (Added)
WebHostFace – started as ridiculously cheap shared webhosting and even faster than SG. Their initial lifetime plans were a great bargain even if you only used them for only a few years. Nowadays, I think their performance has dropped greatly to be more in line with the usual shared hosting.
A2Hosting – largely touted as a “great service” but many complain of long TTFB. I’ve used it and it’s definitely not on the same level as SG. Their turbo caching isn’t much, either. It is cheaper than SG though.
GNUHost (UK) – I heard good things about this one but haven’t tried it.
Veerotech – haven’t tried them yet but have heard good things. They’re a smaller large company (does that even make sense?).
Krystal (UK) – good speeds and cheap pricing, also use LiteSpeed servers. I recommend this for UK folks. I personally tried it.
GURU (UK) – another good UK host. Some people like GURU better than Krystal. They use LiteSpeed and allow crawling.
My personal recommendation:
Shared hosting is great for new websites with no traffic. It’s easy to use, allows you to host/manage many sites, and still pretty fast if you pick a good webhost. But the moment you get over 25,000 visits/month (and assuming you make some $$$), you should really consider moving to a VPS. The speeds are much faster and a magical world of difference for those who’ve never tried VPS before.
Those of you who aren’t married to cPanel and don’t need to have email hosting, should really just go with RunCloud or Cloudways. It’s far more performance and service at similar cost ($10–25/month). Should you want to ADD emails to Cloudways, you can go with G-Suite or use their Rackspace add-on, etc. Using a professional email service gives you much higher deliverability. If you’re a true techie, you can also do RunCloud.
I would also like to do a huge shoutout for the smaller webhosting companies. I’ve come to find they always offer better pricing and great service than the major ones who don’t care if you leave.
Unmanaged VPS Hosting (best speeds & cost-efficient, but requires sys-admin)
Amazon Lightsail – expensive and not as fast, with terrible UI. But can be useful if you want tighter integration with other AWS services.
DigitalOcean – best pricing and sexiest interface, solid speed/uptime. Considered by many as the leader of the price war (race to the bottom for cheapest VPS). They are still quality but with slight issues for downtimes or slow to roll out old hardware. Also some bad PR and customer service here and there (shutting clients down erroneously).
Prgmr – no-nonsense VPS for techies. Great pricing, solid speed and uptime.
Linode – my favorite. Solid, reliable, no BS, always faster HDparm reads. They used to have some power outage problems but they are few and far between. Linode/Vultr/DO are top 3.
RamNode – try them if you want to check out a smaller company (cheaper pricing), I like their DDOS-filtered IP protection. It’s a great idea if you’re running a webhosting business.
Scaleways – not the best VPS provider (slower speeds, disks, CPU, etc), but still serviceable and offers $2.50/month micro-plan. Scaleways is considered really bad.
Webdock.io – semi-managed solution. I haven’t tried yet but they’re now on my radar for some interesting value points.
Vultr – similar to Scaleways (slower speeds, disks, CPU) but offers small $2.50 micro-plans and also bare metal servers. Vultr is however better in some parts of the world and considered even faster/more reliable than DO by some, especially since their recent upgrade. Don’t bother with their DDOS protection; I hear it isn’t very good. I did have dropped network packets in their Sydney (AUS) data center.
Lesser-known unmanaged VPS hosts:
LunaNode (CA) – nice VPS provider out of Eastern Canada (only) with good pricing, many configurations, and good reviews on the web.
UpCloud (FI) – friendly Finnish company with servers all over the world; great speeds, pricing, and industry-leading SLA. I hear great reviews about them being faster (record-breaking IOPS) although my personal tests showed otherwise. Many customers switched over to them happily from Linode and DO. They have a nice UI, but I don’t like how the web console can’t copy-paste and is stuck on the Finnish keyboard. Chat support is nice!
My personal recommendation:
When buying a VPS, choose a company that doesn’t deal with shared hosting. For whatever reason, I find pure-VPS/dedicated hosts to be more knowledgeable and specific to the niche of high-performance servers and 100% up-time as opposed to shared hosts who often over-sell their servers and have rampant downtime or performance degradation.
It’s an important distinction to make that shared hosts are focused on features, ease of use, and customer service. VPS hosts are focused on hardware and speed. Basically, they are 2 entirely different businesses.
In case you’re wondering about different VPS providers: DO, Linode, and VULTR should be your industry baseline standard. From there, all the other backbone providers will differ in performance, pricing, or security features. They might also be the same for their base plans but differ on add-on pricing (they charge more for IPs, DDOS-filtering, etc).
You should beware of new VPS providers offering huge discount pricing. Most of the time, the pricing and deals are legit and you will get incredible hardware at a great price. The big issue is knowing how well they’ll scale into the future. Many of them are really small-time providers mixing different hardware which will be harder to maintain over time and harder to get consistent upgrades/maintenance.
There are ALSO “managed VPS” solutions which are different from the options listed above which are the usual “unmanaged VPS”. Managed VPS allows you to have both VPS speeds without having to configure the server but comes at a high price that I think isn’t worth it. In case you’re wondering, I use “unmanaged VPS” and hire a sys-admin to handle it for me.
Managed VPS Panels aka “Cloud Panels” (high performance, low-cost, but for techies)
RunCloud.io – most mature UI and has both Apache-NGINX and pure-NGINX stacks. Performance has improved a lot since their latest RunCloud Hub caching solution (much more on-par with GridPane and top-tier NGINX performance stacks). I find them cheaper, faster, and more user-friendly than most average cloud-panels. Really full-featured panel; great for dev environment. Awesome support. My favorite choice in this tier.
GridPane:
Good performance; clean/minimal but useable UI. Intro pricing is much higher than others ($100/month?), so only a reasonable deal if you have many servers. I cannot in clean conscience recommend them to anyone. It’s a good product, but not a good value for your money. Most of all, you feel like you’re constantly being upsold. (Updated — more detailed and more direct)
GP CEO Patrick Gallagher is known for terribly unprofessional attitude (publicly trash-talking or leading mobs against anyone criticizing any part of GridPane), but the rest of the team seem like nice people.
While this panel makes many promises and is aggressive with feature development, their latest features can be buggy. Despite their “Transparent Pricing” label, it’s anything but. Their pricing and business model changes all the time (like 2–3 times per year). I never know what it is at any point in time.
They also have an annoying cliché “online marketing” sales model where they’re always trying to upsell you to some expensive training program or secret products/services. I prefer a company that focuses on hosting and profits via hosting (not constant side-gig upsells).
The GridPane lifetime LTD plans have turned out to be a scam IMO. As all new features they develop are not included, but require a separate ongoing subscription payment. It’s no surprise that many previous holders of their LTD licenses have abandoned their $3k investment and looked for new hosting elsewhere. (Added)
SpinupWP – new cloud-panel company by respected WP plugin house. Fast, but overly-simple UI. Feels like it has no features, slightly overpriced IMO. Great if you want a simple server and Digital Ocean. Delicious Brains recently sold off all their plugins to focus on this business, so we can expect aggressive growth here soon.
Cloudways – popular managed cloud hosting, fair price, average performance but good enough for most folks, full-featured control panel (good for noobs and sys-admins). Most hassle-free option here for non-techies. Their support is the best in this hosting category. Friendly and helpful but will not teach you how to use WordPress! Make sure you purge/disable Varnish during development. They do have some buggy issues from time to time.
Laravel Forge – another high-performance option. Similar to RunCloud.
ServerPilot – an established panel in this industry. Trusted by many pros. Their UI looks more plain, which some folks like. They now have a cheap 1-server plan (unlike RC/GP).
Moss.sh – haven’t tried it yet but really cool vibe. I like the branding. UPDATE: they are shutting down Sep 1, 2020. And update again, they are NOT shutting down. (Hooray!)
Ploi.io – reminds me a lot of RunCloud. I haven’t tried yet but heard nice things.
ClusterCS – same as others but this one also allows easy cluster-deployment for building your own HA environment without having to configure all those proxies and what not. How cool!
My personal recommendation:
These solutions were originally created for techies to manage their “unmanaged” servers from Linode/DO/etc for very cheap but still great performance. They used to be extremely technical and required a lot of server skill to use but have since become more and more approachable for regular power users.
If you’re a developer or at least WordPress and Google-expert, these are a fantastic/cost-efficient way to have your own powerful VPS server without having to do server management or muck around in the command line.
Premium/Managed WordPress Hosting (fast, but expensive & limitations)
Amazon EC2 – expensive/weak to me, horrible over-technical UI.
Flywheel – promises to be better than WP Engine but user comparisons are mixed. Nice UI. Doesn’t allow different PHP settings per site, stupid! I only recommend it if you have one tiny site. ($14/month & up)
Kinsta – great branding and unanimously faster than WPengine/Flywheel although I’ve heard a few bad reviews about downtimes. As of AUG 2019, I can say they’ve definitely gone downhill and even slower now, with lower resource limits but still better than WPE. ($30/month & up)
Pantheon – incredible speeds and service. Servers switch to inactive mode when websites get no visitors making 1st visits slower as the server “wakes” again. ($35/month & up)
WP Engine – best marketed and most popular premium WordPress hosting. They’re like the GoDaddy of managed hosting. Not the fastest, have some plugin limitations, and many issues that people complain about. Non-techie users find them to be amazing (compared to crappy shared hosting), tech users find them to be sub-par (compared to VPS) and limiting. FYI: they use Linode servers and add proprietary caching layer; you can beat them with a $5 VPS. ($35/month & up)
Closte – good performance but pricey. Some technical issues here and there and also rude-ish French support. Some people like them while others always run into problems. I don’t recommend them for non-techies.
Rocket.net – high-performance host with edge-caching capabilities. Pricey but works well and easy to use. Can be affordable enough if you only have 1 or 2 critical sites but definitely too pricey if you have many small ones.
Lesser-known premium/managed hosts:
RaidBoxes.io (EU) – nice host out in the Germany/Switzerland area using NGINX. Fast servers and excellent super fast/friendly support. My only annoyance is that they edit core files (so be careful if you ever migrate away from them).
My personal recommendation:
Unlike cloud hosts which give you a server with limited resources (hardware lease) and let you do whatever you want, premium hosts give you a traffic limit and guarantee high speeds (speed service).
Maybe it’s the DIY-techie in me, but I don’t like premium WordPress hosting. It’s really expensive if you have: 1) lots of traffic, 2) more than one site, or 3) an uncomplicated site. Go to WPengine and see how much it costs to host ONE site with 500k visits/month (answer: over $300/month). For a third of that price, I could get my own VPS and host a dozen of those. And assuming the sys-admin setting up the server is experienced, I could get those sites to load even faster than on WPengine.
Non-techies go with premium hosting because it’s the easiest way to set up a super-fast host. It comes with fancy panels and is really easy to use, no configuration. Kind of like buying a new computer and just turning it on. Getting a VPS is more like buying individual computer parts and putting it together yourself. Some tech-savvy owners choose VPS because they love messing with tech things and appreciate the benefits-to-cost ratio. Other tech-savvy owners respect the complexity involved and prefer to pay someone else to deal with it (thus choosing premium hosting).
To those who say managing servers is too much work: setting up a server takes like 2 hours to build out and a few minutes of maintenance every couple months. How else do you think these “managed hosts” stay in business? None of them are proactively maintaining your server either. You call them when you have an issue and THAT’s when they fix things. Same goes for having your own server and sys-admin. Only difference is you save a ton of money.
Pagely – incredible speeds but REALLY pricey. ($299/month & up)
Pantheon – is here in ultra-premium space as well. ($150/month & up)
ServeBolt – still pricey but reasonable with ultra fast enterprise-grade performance. I like them. ($150/month & up)
WordPress VIP – overpriced to me. ($1,000 & up)
My personal recommendation:
These guys are the absolute most expensive and most professional tier of WordPress hosting you can get. Super fast TTFB, great performance even for many dynamic requests. They’re more for huge sites — like 10 million hits/month and up, or really big stores. If you have fewer visits or a smaller site than that, you can save a whole lot of money with other providers.
The first questions are: why are they SOOOO expensive and what do they offer that’s different from the other (much more affordable) premium hosts?
To start with, their server hardware and configurations are extremely optimized for performance. They tweak the servers for every possible bit of speed. Compared to other plans, it may not seem like a lot of resources but your configuration is much more customized than other hosts. They write their own PHP libraries/handlers — it’s almost like running their own custom server software. Things like DNS are managed in a proprietary way instead of just leaving that to each customer. They have their own in-house panels.
For the most part, they’re complete overkill for 99% of customers out there. But suppose you had a huge worldwide business and don’t have expert sys-admins on hand, these guys are perfect for you. Their servers can handle tons of traffic and also huge traffic spikes. Also, these server plans are not limited by traffic like WPengine/Flywheel/etc. These servers can handle virtually millions of hits, instead of WPengine and the others charging by traffic. 400k visits/month costs you $290/month at WPengine whereas with Servebolt, your site could easily handle 400k visits/day with their $150/month plan. So in theory, these plans could actually be higher performance and even cheaper than other hosts!
All those top guys will be about the same speed/performance — you should try Servebolt (I like them).
Pay close attention to what their SLA says — ideal is at least three 9’s for that amount of money you’re paying. Many of them market themselves as “HA” but only offer 99.9% which is the same as most backbone providers.
Ask them if their IPs are already DDOS-filtered or if that’s an extra cost.
All of them will be more than happy to load up demos for you to pit against each other.
Might also be a good idea to test their support and see how quickly you can get access to a level 3 tech.
If you have tons of traffic, you should not be paying by traffic count (you should be paying for the stack management only). Keep in mind that some of the cheaper-priced ones offer limitations somewhere (visitor count, storage size, number of websites, bandwidth, CPU processing limit, etc).
If you have a budget of $5k, that’s fantastic but you really don’t need to spend that much. You could easily get the same performance if not faster for a small fraction of that. And not pay for all that overhead. Hire someone — a direct level 3 tech who can provision and manage the server for you. Whatever other add-ons you like, you pay a much smaller fee.
Bad (or Mediocre) Webhosts
These are all the crap hosts. Avoid them, no matter what they promise. I’ve had direct experience with every company here through my own accounts or client/friends accounts. And yes, I’m well aware the companies below might have many happy users.
1and1 – yes, it’s bad.
20i (UK) – typical low-tier super cheap host… and super slow.
ASmallOrange – used to be good but turned terrible when they were bought out.
A2 (VPS) – weak, expensive. Sucks compared to others. Their 8 “vCPU” is weaker than even 4 CPU from typical VPS hardware providers (DO, Linode, etc).
BellHosting – BAD!
BeyondHosting – bad hardware, bad service, overpriced.
BigScoots – slow and lots of downtime.
BlueHost – customer service improved but servers are still slow. Awful!
canspace.ca – really slow (even with no traffic) and lots of intermittent downtimes.
DreamHost – great promises but mediocre hosting speeds, awful control panel and downtimes, but great customer service.
EasyWP – NameCheap’s cheap shared hosting service. With a clean website design and using the trendy “managed hosting” label. No, I don’t recommend it. I also think it’s too pricey for cheap tier. (Added)
EIG companies – too many to list, avoid all EIG-owned hosting companies. Terrible service.
FastComet – complaints about being slow, or that they’re great until they have random downtimes.
Godaddy – they’ve improved over the years but still poor speeds, UI, and overall service. Yes, even their GoDaddy managed hosting sucks.
GreenGeeks – I love their mission of ECO-friendly and clean energy. Their hosting, I’ve heard mixed results about. Some people say really helpful, fast, and great service. Others say the service is annoying and they can’t wait to get off. One thing for sure, many people feel their pricing and refund policies are manipulative. Just from looking at their site, I’d guess they are mediocre-performance shared hosting. Not bad, not great.
Hetzner – hardware vendor in Germany popular for their low prices. Some feel they’re a great bargain for the price (super cheap dedicated servers) whereas others feel they have horrible support, issues with unfair billing and interface, also annoying technical/hardware issues. Their performance is subpar for me so I don’t consider them but do agree they are cheap.
Hostgator – oh no. Now owned by EIG, same like BlueHost.
Hostinger – seemed like a friendly new outfit (and their current panel design seems smooth, looks like they copied RunCloud). But I saw them get kicked out of Facebook groups for marketing too aggressively and also making shill reviews. (Their spam posting happened in my Facebook group, too!) Then I also heard of angry customers — some complaining about speed, others about service. Oh and these clowns only give you a free SSL for the 1 site, the others you have to pay! (No other legit webhost does this bullcrap.) The first time I went to their site, I saw a Cloudflare 502 error. Hmmmm… (Updated — added note about RunCloud panel copy)
Hostnet.nl – terrible speed and customer service.
Incendia Web Works – smaller (but great) company run by knowledgeable system expert Budd Grant. Great if you have one site and only one site to focus on. It’s not defunct but who knows, maybe he’ll start another.
InMotion hosting – slow and bad service, horrible VPS. Also running vastly outdated software (old PHP). I move about 5–10 clients away from them every month.
Ionos (by 1and1) – sucks! Super cheap… what did you expect?
InterServer – mixed reviews.
KnownHost – known to be bad! There are some good reviews out there.
LiquidWeb – absolutely horrible performance, but polite customer service. Gone downhill since they acquired WiredTree as well as other companies. I move about 5–10 clients away from them every month. Destroyed many acquired companies (like WiredTree). All their plans seem overpriced except maybe their bare metal servers, which are the only ones I would try from them. They’re like the GoDaddy of server hosting.
LunarPages – average.
Media Temple – used to be good… then they got acquired by GoDaddy. Now it’s in the shitter.
NameCheap – better than Bluehost/EIG but still slow.
Network Solutions – bad!
nosupportlinuxhosting – cheap but good webhosting (with no support) for only $1/month per website. Small 1GB space limit, which is more than enough for small sites. Great option for web-techies wanting to get up and running for cheap. (They got hacked and closed down their service. No longer running!)
OVH (VPS) – bad! Bad service, stuck IO, frozen boxes, reboot issues, slow disks, server crashes, many complaints out there.
Pressable – supposedly a “premium service” but I found it to be slow.
Pressjitsu – I really wanted to like these guys (they know their stuff) but their stack was underwhelming for me. Better than shared hosting but a step behind the usual “managed” tier like WPengine/Kinsta.
Rackspace – used to be good but went downhill.
Site5 – it’s gone downhill ever since getting bought out (by GoDaddy?), super slow. Many users switching away.
SmartHosting (UK) – another UK one, like Krystal and GURU, and some people like SmartHosting better than Krystal as well but they’ve since been bought by Krystal and some people say they’ve gone to crap.
SSD Nodes – on my radar. Love the website and vibe, heard mixed reviews. Some people are happy with performance and uptimes, others complain about slow speeds (oversold servers), confusing pricing, and poor support.
WiredTree – has been really bad since the acquisition.
VentraIP – only tried a few times and it was usually slow, or average at best. (Added)
VPS.net – horrible, tons of downtimes. These guys are the “shared hosting” of VPS providers.
Wedos (CZ) – very cheap and very slow. Don’t use it.
WPMU hosting – the same guys behind WPMU DEV. Somebody from our Slack group tried it and said his site was 4 seconds slower. Hahaha, not surprised.
WPX Hosting – the owner is well-intended, creating WPX as a superior alternative to overpriced/poorly-supported shared hosting out there. Most people are happy but the ones who aren’t… are really unhappy. I’d say they’re comparable to SiteGround (ok speed, great support). They aren’t good for big sites, even their big VPS plans. I often have backup issues with them, sometimes large sites, sometimes even small sites throw errors when trying to backup even a 40MB database. Their support is always helpful but I hate that I can’t do many basic things.
My personal recommendation:
Understanding why these webhosts are “bad” can be the most confusing thing for new website owners. On one hand, you have “expert” sites saying such and such company is “HORRIBLE, AWFUL, NEVER USE THEM!” and on the other hand, you see hundreds of “trusted” review sites showing thousands of happy customers and many 9.5/10 scores. How do you know who to trust?
Haha, you can trust your own experience or mine. Most people don’t listen and will go for the super cheap hosting with the 75% OFF promo code. The server may be fine for 2 months, or even 2 years, and then slowly degrade. Your site keeps getting slower and customer support will tell you it’s because of your theme or your plugins (which could be true). You’ll even hit downtimes on a monthly, weekly, or even daily basis. Your host will assure you it’s only a minor server upgrade and will be up and running better than ever!
At some point, you get fed up and start asking around. Your friend who just signed up with some other host gives you an affiliate code, and you leap all over again — but the cycle only continues. You get bad service again and can’t figure out how to find a decent host. How is this happening?! It’s because these big-name hosts pay huge affiliate commissions. That’s why you see them promoted by so many bloggers out there. An Amazon link might only net them a couple of bucks but a web hosting referral link can earn up to $150 per sign-up.
On My Radar
These are webhosts that I heard of but don’t have any concrete opinion of their service yet.
BunnyShell – reminds me of RunCloud. I like their polished website. Their vibe feels really professional.
10Web – can’t they get rid of that FOUT issue on their website? It looks so unprofessional.
How to Research Webhosts
Looking up established webhosting companies
Check out the sites below to see what systems techs are saying about them.
www.lowendtalk.com – many sys-admins and webhosting experts, many new company deals
Looking up new webhosting companies
How do you research a new hosting company? With new companies that just popped up, you can’t. You have to trust in their branding and the people behind the brand. And not only that, but you have to trust that they’ll have the same enthusiasm for low pricing and great service in 5 years. Many new webhosts start out great but then start over-crowding servers to increase profits or don’t make enough to pay for quality support techs as their service grows. As expected, performance and service goes down so profits can go up!
Is there a way to technically measure them? Yes, you can ask them questions like how many resources per server, per account, etc. You can look up the TTFB’s, use their trial period to check disk speeds, how long to process queries, how many requests per second, etc. It’s a great idea but not something I can bother with. For me, when dealing with companies I don’t know, the biggest thing I’m looking for is how reliable they will be over the years. And only when I know they’re reliable will I start to compare CPU, disk speeds, max requests, etc.
Understanding Load Testing | Browser Load Testing | Stress Test of Website
What is load testing?
Load testing is bench-marking a website to see how it performs under various loads.
For example, a test may simulate an increasing number of concurrent visitors landing on your site. It will also record how your site handles them and records them for your reference.
Example – load tests at LoadStorm: Metrics measured include average response time, peak response time, and error rate (image source).
What types of “load” are tested?
Depending on the tool you choose to load test your site with, each may come with different features. The most basic will simply involve simulating an ever-increasing load and halting when your site crashes.
Other tools may be capable of generating a simulated load that mimics different user behaviour, such as performing queries, changing pages, or loading other functions. Some may even be able to map out logical flows for each individual scenario.
A load test or stress test is measuring how many visitors your site could handle. Technically Requests per second!
This guide is all about load testing WordPress sites, some tips on how to handle sudden spikes, and how I handle it.
Why you should Load Test?
What happens when your blog posts go viral? You’re going to get tons of traffic! This is what happened to me when one of my posts gets featured on Hacker News.
Well, 237 real-time users are not that great, I’ve seen bloggers with 1k-2k real-time users!
Unless you properly load test a site, you don’t know whether all users are able to open your site during these spikes.
Trust me, only a few hosting providers in this world can’t handle this! (listed at the bottom).
Before Browser Load Testing
Browser Load testing is done by sending fake users to your website/server. Here are some points that you need to consider before running a load test.
Some hosting providers charge based on the number of users/visits.
While load testing your site may become unavailable to some users based on the load capacity of your server (that’s what we’re going to test).
How to Load Test a WordPress website?
There are several tools and services that can do a load test. In this guide, we’re going to use Loader.io.
Why Loader.io?
Free (freemium)
Supports up to 10k users in the free plan
Easy to use interface
Supports incrementing users
Cloud-based
Developed by SendGrid (a leading email service)
Create a free account and verify domain
Create an account on Loader.io and verify your domain. You’ll need to download a file and upload it to the root of your WordPress directory (verification via DNS is in their paid plan).
Create a new test
Now let’s create a new test (aka load test) as follows:
Note the “Test Type”. There are multiple options like clients per test, clients per second, and maintain client load.
Maintaining client load will start sending zero users and gradually increase it second by second. In such a way we can make sure that at what point it breaks!
Analyzing Test Results
Once your test is complete, you’ll get a report like this:
The key element we’ve to look for is the ‘Response Counts’. The counts other than success means that many requests failed.
Luckily none of them failed for me! (I don’t believe in luck, learn how I did it below).
How to handle High Traffic in WordPress?
As you can see I was able to test 10k users per second with a 100% success rate. The main trick that helped to achieve this is to cache HTML pages in Cloudflare.
Even though this trick works pretty well for me, not everyone can implement it if you have a lot of dynamic content. In such caches here are some tips:
Never use shared hosting. Use a VPS server like Cloudways or managed hosting providers like Kinsta. These guys really know to handle scaling and handle traffic
Implement Redis/Varnish caching
Offload the server load using a CDN. Use Cloudflare (free) or any plaid ones like BunnyCDN or KeyCDN
Create a static version of pages. Use cache plugins like WP Rocket or WP Fastest Cache
Compress images
Minimize HTTP requests
Conclusion
It’s very important to run a load test and make sure your WordPress site is ready to handle high traffic. Otherwise, you’re going to lose some precious users!
Running a load test is pretty easy as we covered. However, achieving high RPS (requests per second) is very hard. I’ll share many more tips across this blog.
On the hunt for the fastest WordPress hosting provider to serve up your WordPress site?
You’ve probably heard about the importance of making your website load fast. It makes your visitors happier; it helps with SEO…it’s just generally really important.
And while yeah, there are all kinds of WordPress performance tips you can implement to make your site load faster, your site’s hosting is always going to play one of the biggest roles in how quickly your site loads (especially if you’ve already optimized the other stuff).
To help you find the fastest WordPress host provider that also matches your budget, we went hands-on with eight popular WordPress hosts and ran real speed tests. The end goal of this post is to help you find a host that can offer you the performance you want, at the price you want.
You’re probably here for the hard data, so we’ll start by sharing all the data in an easy-to-compare table format.
Then, we’ll dig into each host in more detail and also share some tips for finding the fastest WordPress hosting for your specific needs.
The Fastest WordPress Hosting providers: What the Data Says If you just want the absolute fastest WordPress hosts based on our testing, here are our three recommendations based on their speed, price, and features (full data and more info below):
To find the fastest WordPress hosting, we set up a real test site at every single one of the hosts on this list. Then, we ran our test sites through a duo of speed testing tools:
To collect the WebPageTest data, we used a simple desktop test from Chicago, Illinois with a native traffic connection. We collected two metrics:
Load Time (Document Complete) – this is what most people think of as a website being “fully loaded”. According to the WebPageTest documentation, it’s “the time from when the user started navigating to the page until the Document Complete event (usually when all of the page content has loaded)”.
Time to First Byte – this how long it takes for the first bit from your server to arrive. It shows how responsive a host’s server is.
We configured WebPageTest to run nine separate tests and take the median value, which should eliminate single-test variance. That is, all of the data in the table above is the median result from nine different tests.
WebPageTest data is valuable, but it only gives the load times for a single “visitor”. However, in the real world, your site will have more than one visitor at the same time.
Because of that, it’s important that your host can load your site just as fast for the 50th visitor as it does for the first one.
That’s where the BlazeMeter data comes in. BlazeMeter simulates 50 “people” visiting your site at the same time. That way, you can see how each host performs under scale.
Here are the details for our BlazeMeter tests:
Test location: Virginia, USA
Visitors: 50
Duration: 5 minutes
Ramp up steps: Visitors increase every minute, starting from zero and building up to 50 active visitors for the last minute.
We’ll share the BlazeMeter chart for each host below. One thing to keep in mind, however, is that most managed WordPress hosts implement some type of firewall/DDoS protection, so some hosts blocked some of the requests in our test.
If you see a high error rate in the BlazeMeter charts, this is the result of an overactive firewall, not necessarily poor performance.
How Our Test Site Was Set Up
To simulate a real site and create a consistent test case, we used the lightweight Airi theme and one of its importable Elementor demo sites.
So, our “full” test site includes:
The Airi theme as the base
A homepage design built with the Elementor page builder
Here’s the exact Airi demo site that we’re using.
Fastest WordPress Hosting: Compared in More Detail
Now that you have a good idea of how each host performs in objective speed tests, let’s take a deeper look at their features as well as Load Impact data to see how they stood up under scale.
Kinsta is a popular cloud-managed WordPress host that uses the Google Cloud Platform to help you host your WordPress site. Kinsta also layers on its own optimized tech stack with Nginx, server-level caching via Fast_CGI, and other enhancements.
In addition to offering stellar performance, Kinsta has one of the best looking hosting dashboards out there, as well as lots of convenient features like:
Automatic daily backups
Easy staging sites
Free SSL certificate and one-click install
Firewalls/malware scans
A free hack-fix guarantee if something gets through
You also get some nice value-adds, such as the addition of a CDN and premium DNS services at no extra cost.
Kinsta’s plans start at $30 per month for a single website.
WPX Hosting is a very interesting option if you need to host multiple WordPress sites. It’s managed WordPress hosting but, unlike most managed WordPress hosts, even the entry-level plan lets you host multiple websites (up to five). It does this for a slightly lower price than competing hosts such as Kinsta and WP Engine.
As the data shows, though, it doesn’t skimp on performance — WPX Hosting ranked second in our tests and wasn’t far behind Kinsta.
All of WPX Hosting’s plans come with:
Free/one-click SSL certificates
A built-in CDN at no extra cost
Automatic daily backups
Malware scans and free malware removal if anything shows up
Staging sites
Your choice of three data centers — USA, UK, or Australia
In terms of prices, WPX Hosting starts at $25 per month for up to five websites. Two things to note about WPX Hosting’s pricing:
They don’t bill you by visitors like many other managed WordPress hosts — you’ll only pay based on your bandwidth and storage.
Staging sites count as full websites for billing purposes. So one production site + one staging site = two websites in terms of your plan limits.
Plan Tested: $10 DigitalOcean plan – 1 GB RAM, 1 processor core
Load Time: 1.522 s
Time to First Byte: 0.115 s
Starting price/mo: $10 (depends on cloud provider)
Cloudways is not a host itself. Instead, it’s a managed hosting service that lets you choose your own cloud VPS provider from a list of options, including:
DigitalOcean
Vultr
Linode
Amazon Web Services (AWS)
Google Cloud
No matter which cloud provider you choose, you’ll get an optimized performance stack, a built-in CDN, and useful features such as:
One-click staging sites
Easy/free SSL certificates
One-click WordPress installs
Automatic backups
The one downside is that Cloudways is a little bit more complicated than your average WordPress host. However, it’s certainly still something that a non-developer can handle — I just wouldn’t recommend it if this is your first time launching a WordPress site.
The big upside is that Cloudways is able to offer exceptional performance for a lower price than all the other top-performing hosts on this list.
For reference, our test site is using the cheapest DigitalOcean droplet, which costs just $10 per month. Your exact speeds may vary depending on the cloud provider that you choose. However, all the cloud providers offer excellent performance. If you’re really obsessed with speed, you can play around with the newly released Vultr High-Frequency servers.
One neat thing is that Cloudways offers a 3-day free trial. So if you’re interested, spin up a test site and see how it works for you.
Note – Flywheel was acquired by WP Engine in 2019. While this has led to some standardization (e.g. in pricing), the two are still run separately and have a separate infrastructure.
Flywheel is a popular managed WordPress host that used to target itself mainly creatives, freelancers, and agencies. However, in recent times, they’ve moved towards a more mainstream audience, and anyone can benefit from Flywheel’s hosting services (though if you do build websites for clients, Flywheel still has tons of convenient features for that).
Like Kinsta, Flywheel uses Google Cloud Platform’s infrastructure to power its plans. Beyond that, they have tons of helpful features like:
Staging sites
Automatic backups
Free SSL certificate
Built-in CDN (extra charge on lower-tier plans)
24/7 support
Flywheel’s plans start at just $15 per month with the Tiny plan, which is the plan we tested. This plan has all the features, but a low traffic limit (just 5,000 visitors). Higher tier plans start at $30 per month. Excluding the Tiny plan, Flywheel’s prices are identical to WP Engine.
As an upshot of the WP Engine acquisition, all Flywheel customers now also get access to the Genesis Framework and StudioPress child themes at no extra cost.
WP Engine is one of the most popular managed WordPress hosts out there. All of the WP Engine plans come with staging sites, automatic updates and backups, integrated CDN, and plenty of other helpful tools.
One neat thing is that WP Engine recently acquired the Genesis Framework and all of StudioPress’ Genesis child themes. These themes are now included at no extra cost as part of every WP Engine plan.
WP Engine’s plans start at $30 per month and go up from there.
InMotion Hosting is a well-known budget host that’s recently made the jump into managed WordPress hosting with a set of affordable plans.
Their plans come with automatic WordPress updates, free SSL certificates, and free backups (automatic on all tiers except the cheapest). And on the higher tier plans, you can also get access to the premium tiers of Jetpack at no extra cost, just like DreamPress offers.
InMotion Hosting didn’t have the best performance in our tests, but its cheapest tier — the WP-1000S plan that we tested — starts at just $5.99 per month with promotional pricing, which still offers good value when you consider the price.
DreamHost is one of the oldest web hosts out there, founded all the way back in 1996. DreamPress, the hosting plan we tested, is DreamHost’s managed WordPress offering.
It comes with daily automatic backups, unmetered bandwidth, and 24/7 support. And on higher-tier plans, you’ll also get a built-in CDN, as well as access to the (normally paid) Jetpack Professional plan at no extra cost.
With plans starting at just $16.95, DreamPress is a good value option. However, you’ll need at least the $24.95 DreamPress Plus plan if you want Jetpack Professional and the included CDN.
SiteGround is a popular WordPress host that manages to combine pretty fast page load times, some managed WordPress features, and great support into one surprisingly low-priced package.
If you’re on a budget and want the best bang for your buck, SiteGround is one of your better options (though I’d still rank it behindCloudways).
While the prices are comparatively low, you still get access to:
The latest technologies, including PHP 7.4+
Automatic WordPress updates
Staging sites (excluding the entry-level plan)
A custom hosting dashboard
Great support
SiteGround’s plans start for as little as $6.99 per month, though we tested the $9.99 per month GrowBig plan. However, make sure to pay attention to the differences between promotional prices and regular prices, as the difference can be large. If you want to use SiteGround, we recommend trying to lock in three years of promotional prices. While it will cost you more upfront, it will save you a lot of money in the long run.
Tips to Choose the Fastest WordPress Hosting For Your Site
When you’re trying to choose the best hosting for your specific needs, here are some things to consider:
Data center locations – while a CDN can mitigate this issue, you still want to find a host that offers data centers near your target readers.
Think about your traffic – if your site is relatively low traffic, you might be fine with one of the budget options. However, for high-traffic sites, you want to make sure your chosen host did great in the Load Impact test. You’ll see that the higher-priced hosts usually differentiate themselves when performing under scale.
Price – finding the fastest WordPress hosting company isn’t just about the overall winner. It’s about finding the best option that fits your budget. Paying an extra $30 per month just to save a couple fractions of a second might not be worth it for you, especially if your site doesn’t get a lot of traffic.
Which Host Should You Choose?
Again, there’s no single winner here — it really depends on your needs.
However, as we indicated at the beginning, Kinsta and WPX Hosting had the best overall performance. Of the two, Kinsta stood out, but WPX Hosting will be much cheaper if you need to host multiple websites.
If you’re looking for something more on the budget end and you aren’t a super technical user, SiteGround is a great entry-level option that will still get you pretty good performance without breaking the bank, especially if you need to host multiple sites. If you just need to host a single website, InMotion Hosting is also a solid option.
Finally, if you’re a little more technical, Cloudways can be a great choice because you’ll get surprisingly good performance for as little as $10 per month. I recommend the entry-level DigitalOcean box if you want the cheapest option. Or, if you’re willing to pay a few dollars more, check out the new Vultr HF servers (high frequency).